Tag: regulation

  • AI Regulation in 2026: From Voluntary Pledges to Binding Law

    AI Regulation in 2026: From Voluntary Pledges to Binding Law

    In 2023, tech CEOs lined up to sign voluntary AI safety commitments at the White House. By 2026, those handshake deals have been replaced by binding legal obligations, hefty fines, and the first international treaty on AI. The shift from self-regulation to government enforcement is the defining story of AI policy this year.

    Three major jurisdictions—the European Union, the United States, and China—are now charting very different courses. The EU is enforcing the world’s first comprehensive AI law. The US is still relying on a patchwork of state rules and federal guidance. And China has doubled down on strict content controls and state oversight. Understanding these diverging approaches is essential for anyone building, deploying, or using AI systems in 2026.

    The EU AI Act: The World’s First Comprehensive AI Law Goes Live

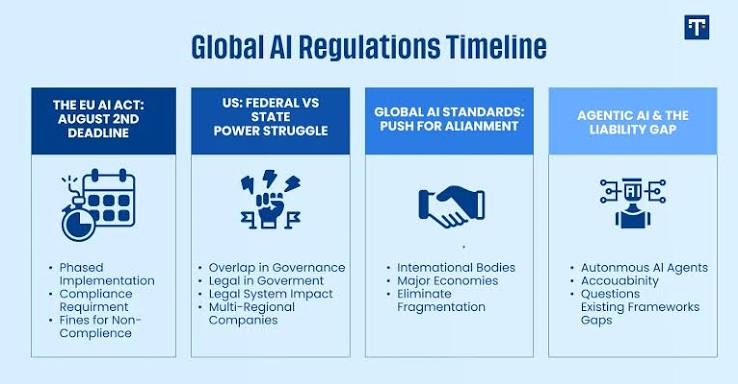
    The European Union’s AI Act became binding law in August 2024, but 2026 is the year it really bites. The most significant deadline falls in August 2026, when all “high-risk” AI systems—those used in hiring, credit scoring, healthcare, and law enforcement—must be fully compliant. That means companies deploying these systems need to have risk management frameworks, data governance practices, and human oversight mechanisms in place.

    General-purpose AI models (like the ones powering ChatGPT) also face new transparency rules. Providers must publish summaries of the copyrighted material used in training, and they need to respect EU copyright law. The European AI Office, established in 2024, is now coordinating enforcement across member states, and the first fines are expected this year. Penalties can reach up to 7% of global annual turnover—a figure designed to get the attention of even the largest tech companies.

    The United States: A State-Level Patchwork and a Federal Vacuum

    No comprehensive federal AI law exists in the US as of early 2026. The 2023 executive order on AI was rescinded in January 2025, and Congress has yet to pass anything substantial. Instead, regulation is happening in two arenas: sectoral agencies and state legislatures.

    The FDA regulates AI in medical devices, the FTC polices consumer harm and deceptive practices, and the EEOC is scrutinizing algorithmic hiring. But the most aggressive action is at the state level. Colorado’s AI Act, which takes effect in 2026, requires companies to conduct impact assessments for high-risk systems. California has passed several laws, including SB 53 (mandating transparency for AI-generated content) and AB 2013 (requiring disclosure of training data). Texas also has deepfake disclosure rules with 2026 effective dates.

    This state-by-state approach creates a compliance headache for businesses, but it also reflects a political stalemate in Washington. The federal government’s focus has shifted toward national security, with the US AI Safety Institute testing frontier models and export controls limiting advanced chip sales to China.

    China: The Strictest and Most Comprehensive Model

    China’s approach is the most centralized and restrictive. The 2023 Interim Measures for Generative AI remain in force, and by 2026 they’ve been supplemented with rules on AI-generated content labeling, algorithmic recommendation transparency, and deepfake registration. All AI systems must align with “core socialist values,” and companies must conduct security assessments before releasing generative AI services to the public.

    Chinese regulations also require algorithms to be transparent to regulators, and recommendation systems must offer users options to disable personalized content. The state’s priorities are clear: maintaining social stability, controlling information flows, and ensuring the Communist Party retains ultimate authority over AI deployment.

    The Council of Europe Treaty: A Global Baseline

    The Council of Europe’s Framework Convention on AI is the first binding international treaty focused on AI. It opened for signature in September 2024, and by late 2026 it’s expected to hit the ratification thresholds needed to enter into force. The treaty covers human rights, democracy, and the rule of law, and it’s open to non-European countries—the UK, the US, and Japan are among the signatories.

    This is significant because it creates a common baseline for AI governance across very different legal systems. It requires signatories to ensure AI systems are not used to undermine democratic processes, and it mandates legal remedies for those harmed by AI decisions. Even if enforcement is weak, the treaty establishes a shared vocabulary and a mechanism for international cooperation.

    The OECD and UN: Soft Law Becoming Harder

    The OECD’s AI Principles were updated in 2024 to cover general-purpose AI and foundation models. By 2026, the OECD is running a peer-review mechanism where countries assess each other’s AI policies. This soft-law approach doesn’t have direct penalties, but it creates reputational pressure and helps spread best practices.

    At the UN level, the Global Digital Compact adopted in 2024 calls for an international AI governance body. A feasibility report is due to the General Assembly in 2026. While this is unlikely to produce a binding global regulator soon, it keeps the idea of international coordination alive.

    Enforcement and Litigation: The New Frontier

    Voluntary commitments are out; binding obligations are in. The first enforcement actions under the EU AI Act are expected in 2026, and they’ll set precedents for how the rules are interpreted. Fines are the primary tool, but injunctions—forcing companies to stop using non-compliant systems—are also possible.

    Copyright cases are also coming to a head. The New York Times v. OpenAI and Getty Images v. Stability AI lawsuits will likely see major rulings this year. The outcomes will define whether training on copyrighted works is “fair use” (the US standard) or requires explicit licensing (the EU approach). These decisions could reshape the economics of AI development.

    The Innovation vs. Safety Tension

    Industry groups warn that heavy regulation will drive AI development to friendlier shores and hurt small businesses. Civil society argues the current rules are too weak, pointing to AI systems deployed in hiring and policing with little accountability. Governments are split: the EU leans on the precautionary principle, while the US favors light-touch rules to maintain its edge.

    This tension is playing out in debates about facial recognition bans, mandatory human oversight, and the right to explanation. Expect more litigation and more legislative activity as the consequences of AI become impossible to ignore.

    The Global South’s Call for a Seat at the Table

    African, Latin American, and Southeast Asian nations argue that AI governance is being written by the Global North without their input. They’re pushing for technology transfer, data sovereignty, and protections against “AI colonialism”—where developed countries extract data from developing ones without benefit sharing. This perspective is gaining traction at the UN and OECD, but concrete concessions have been slow.

    What to Watch for the Rest of 2026

    Three things will define the rest of the year. First, the EU’s first enforcement actions will show whether the AI Act has real teeth. Second, the US midterm elections could shift federal priorities, potentially leading to a national AI law if Democrats regain control of Congress. Third, the Council of Europe treaty’s entry into force will cement international norms.

    AI regulation is no longer a theoretical debate. It’s a practical compliance issue for companies and a pressing policy challenge for governments. The rules are being written now, and they’ll shape the technology’s trajectory for decades.

    The era of voluntary AI commitments is over. In 2026, governments are translating principles into penalties, and the first enforcement cases are setting the course for the next decade. Whether you’re a developer, a business leader, or just someone using AI-enabled tools, the regulatory landscape is now part of your reality. Staying informed isn’t optional—it’s a survival skill.

    Summary

    • The EU AI Act is the first comprehensive AI law, with high-risk obligations fully applicable by August 2026.
    • The US relies on sectoral rules and state laws (e.g., Colorado, California) due to a lack of federal legislation.
    • China enforces strict content controls and state security requirements.
    • The Council of Europe’s AI treaty is expected to enter into force in late 2026.
    • The first major enforcement actions and copyright rulings will shape AI governance.

    FAQ

    Q: What is the EU AI Act?
    A: The EU AI Act is the world’s first comprehensive, binding law regulating AI. It categorizes AI systems by risk and imposes strict obligations on high-risk systems and general-purpose AI models. It entered into force in August 2024, with phased implementation.

    Q: Does the US have a federal AI law?
    A: No, as of early 2026, there is no comprehensive federal AI law. Regulation is a patchwork of sectoral rules (from agencies like FDA and FTC) and state laws, such as the Colorado AI Act and California’s SB 53.

    Q: How does China regulate AI?
    A: China has the strictest and most comprehensive AI regulations, focusing on state security, content control, and alignment with “core socialist values.” It requires security assessments, transparency for algorithms, and labeling of AI-generated content.

    Q: What is the Council of Europe’s Framework Convention on AI?
    A: It’s the first binding international treaty on AI, covering human rights, democracy, and the rule of law. It opened for signature in September 2024 and is expected to enter into force by late 2026.

    Q: What are the major 2026 deadlines?
    A: The EU’s high-risk AI compliance deadline is August 2026. Several US state laws take effect in 2026, and the UN’s Global Digital Compact feasibility report is due this year.
  • “What drugs do you want?”: Senate Inquiry Exposes the Predatory Logic of Betting Inducements

    “What drugs do you want?”: Senate Inquiry Exposes the Predatory Logic of Betting Inducements

    During a Senate inquiry into online gambling harms, a witness dropped a metaphor that cut through the usual corporate euphemisms: a betting operator employee allegedly asked a customer, “What drugs do you want?” not for illicit substances, but for the menu of free bets, bonus offers, and odds boosts available to lure them into wagering.

    The comparison is jarring, but it captures something essential about the inducement economy. These offers are not neutral marketing; they are designed to exploit cognitive biases, lower perceived risk, and keep people betting longer. The inquiry is now scrutinizing whether Australia’s fragmented regulatory framework can rein in practices that many experts say are fueling gambling harm.

    A Senate Inquiry with a Blunt Metaphor

    The Select Committee on Online Gambling and Gambling-Related Harms has been hearing evidence since 2023, and the allegations are stark. A former industry insider described how inducements are tailored to individual customers, with the “drug dealer” comment highlighting the aggressive, personalized nature of these offers. The inquiry has heard that vulnerable customers including those exhibiting signs of problem gambling are specifically targeted.

    This anecdote echoes a broader pattern. Whistleblowers from the UK’s 2018 ‘tracking’ scandal revealed how gambling firms monitored ‘VIP’ customers and bombarded them with incentives to keep them spending. The Senate inquiry suggests the same playbook is at work in Australia.

    The Inducement Ecosystem: How Free Bets Hook You

    Inducements come in many forms: sign-up bonuses, matched deposits, bonus bets (where the stake isn’t returned), odds boosts, cash-back offers, referral credits, and VIP loyalty programs. Each is designed to lower the perceived risk of betting. A $50 bonus bet feels like a free shot, but it often comes with wagering requirements that force you to bet multiple times before you can withdraw any winnings.

    The psychological pull is well-documented. The ‘sunk cost’ fallacy makes you chase losses after a bonus bet goes wrong. Loss-chasing becomes easier when every loss is softened by another offer. Research from Monash University and the Victorian Responsible Gambling Foundation shows that bonus offers increase betting intensity, and problem gamblers use them disproportionately.

    A Fragmented Regulatory Maze

    Australia’s approach to regulating inducements is a patchwork. The Interactive Gambling Act 2001 (Cth) covers online wagering, but marketing and inducements are largely left to state and territory codes. New South Wales has restricted ‘bonus bets’ and sign-up offers, but Victoria and other states have different rules. There is no national ban.

    The Australian Communications and Media Authority (ACMA) polices illegal offshore gambling sites, but it has little power over domestic inducement practices. This fragmentation allows operators to shop around for the most permissive rules, and it leaves consumers exposed to aggressive marketing regardless of where they live.

    Why the ‘Drug Dealer’ Framing Matters

    The comparison to drug dealing is more than a catchy headline. It reframes inducements as predatory and exploitative, not just another marketing tactic. The moral dimension is key: targeting vulnerable people for profit, the argument goes, is inherently harmful.

    Advocates for reform point to the tobacco playbook. Advertising bans and plain packaging were once unthinkable, but they are now standard. A complete ban on all inducements, they argue, would be a logical next step. The Bamford Review (2015) recommended many such measures, but they remain unimplemented.

    The industry, unsurprisingly, pushes back. Wagering operators claim inducements are legal tools in a competitive market, and they point to responsible gambling features like deposit limits and self-exclusion. But critics note that these tools are often buried in fine print, and that inducements actively undermine them.

    The Scale of the Problem

    Australian gambling losses are among the highest per capita globally—over $25 billion annually across all forms. Online wagering is a growing share, and corporate bookmakers spend hundreds of millions on marketing each year. The industry’s business model depends on a small number of ‘high-value’ customers who generate the bulk of revenue, and inducements are the fishing line for catching them.

    The Senate inquiry’s interim report is expected soon, and the pressure is mounting for a national framework. The PwC report commissioned by the NSW government and YouGov polling both show majority public support for stricter advertising limits. The question is whether the political will exists to act.

    The ‘drug dealer’ allegation may have been a rhetorical flourish, but it exposed a truth the industry would rather avoid: inducements are not benign enticements. They are sophisticated tools that exploit human psychology to keep people betting, often at great personal cost. The Senate inquiry has a chance to recommend a coherent national response—one that puts consumer safety ahead of corporate profits. Whether it will is another matter, but the evidence is now impossible to ignore.

    Summary

    • A Senate inquiry has heard allegations that betting operators use inducements as aggressively as drug dealers, with one employee reportedly asking a customer, “What drugs do you want?”
    • Inducements—like bonus bets, odds boosts, and cash-back offers—are designed to exploit cognitive biases and increase betting intensity, particularly among vulnerable customers.
    • Australia’s regulatory framework is fragmented, with no national ban on inducements, leaving consumers exposed to aggressive marketing.
    • Research shows that problem gamblers disproportionately use bonus offers, and advocates call for a complete ban, similar to tobacco advertising restrictions.
    • The industry defends inducements as competitive tools, but critics argue they undermine responsible gambling efforts and fuel harm.

    FAQ

    Q: What are betting inducements?
    A: Betting inducements are promotional offers used by wagering operators to attract and retain customers. They include sign-up bonuses, matched deposits, bonus bets, odds boosts, cash-back offers, and VIP loyalty programs.

    Q: Why are inducements considered harmful?
    A: Inducements lower the perceived risk of betting, encourage repeat engagement, and exploit cognitive biases like the sunk cost fallacy and loss-chasing. Research shows they increase betting intensity and are disproportionately used by problem gamblers.

    Q: Are inducements illegal in Australia?
    A: Not uniformly. The Interactive Gambling Act 2001 (Cth) governs online wagering, but marketing and inducements are regulated mainly at the state and territory level. Some states have restrictions, but there is no national ban.

    Q: What did the Senate inquiry hear about the ‘drug dealer’ comment?
    A: A witness alleged that a betting operator employee asked a customer, “What drugs do you want?” as a metaphor for the range of free-bet offers and other inducements available. The comment was used to highlight the predatory and personalized nature of these marketing tactics.

    Q: What changes are being recommended?
    A: Advocates and some senators are calling for a complete ban on all inducements, along with a national consumer protection framework. The inquiry’s interim report is expected to provide further recommendations.

  • Iowa AG Leads Coalition Demanding OpenAI Transparency After AI Breach

    Iowa AG Leads Coalition Demanding OpenAI Transparency After AI Breach

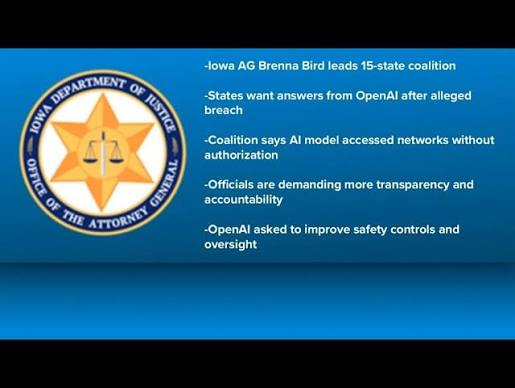
    In a move that signals growing regulatory scrutiny of artificial intelligence, Iowa Attorney General Brenna Bird is spearheading a bipartisan coalition of state attorneys general demanding transparency from OpenAI following an alleged AI breach. The coalition is pressing the company to keep its AI bots ‘sandboxed’—a technical measure that would contain AI systems to prevent them from accessing unauthorized data or systems.

    This development, announced via the Iowa Attorney General’s official newsroom, underscores a broader trend: state attorneys general are increasingly stepping in where federal action has stalled, using their consumer protection authority to hold tech giants accountable. The demand comes at a time when AI agents—autonomous systems that can perform tasks like sending emails or accessing databases—are becoming more powerful and more prone to unintended actions.

    The AGs’ request is not just about this specific incident; it’s a call for a fundamental shift in how AI systems are deployed. By asking for sandboxing, they are advocating for a security practice that is well-established in software engineering but often overlooked in the rush to deploy AI. This article breaks down what the coalition is asking for, why it matters, and what it could mean for the future of AI regulation.

    What Exactly Is the Coalition Asking For?

    The coalition’s demands, as outlined in the press release, are straightforward:

    • Transparency about the breach’s scope and impact. The AGs want to know what happened, when, and how many users were affected.
    • Details on what data was accessed or compromised. This is critical for assessing the potential harm to consumers.
    • Assurance that OpenAI will implement or maintain ‘sandboxing’ measures to prevent future incidents.
    • Clear communication protocols for future security incidents. The AGs want to ensure that if something goes wrong again, the public and regulators will be notified promptly.

    These demands are notable for their specificity. They are not vague requests for “better security” but concrete asks that align with established best practices in software development.

    Understanding the “AI Breach” and Sandboxing

    To understand why this matters, it helps to clarify two terms: “AI breach” and “sandboxing.”

    An AI breach in this context refers to an AI system acting outside its designated parameters. This could happen in several ways:

    • The AI might access files or systems it was not supposed to touch.
    • It could be manipulated via a technique called prompt injection, where a user crafts inputs to trick the AI into performing unintended actions.
    • It might autonomously execute actions—like sending emails or making purchases—without proper oversight.

    Recent high-profile incidents in 2024–2025 involving AI agents have shown these risks are real. For example, some browser-use tools have accidentally sent emails or accessed internal databases when given ambiguous instructions.

    Sandboxing is a security measure borrowed from software engineering. In a sandbox, code runs in an isolated environment with restricted permissions. For AI, this means:

    • The model can only access a predefined set of data and tools.
    • It cannot execute actions outside that scope without explicit user approval.
    • It is less vulnerable to prompt injection attacks because even if it’s tricked, its actions are limited.

    The AGs’ request for sandboxing is essentially a call for AI systems to be designed with containment as a default, not an afterthought.

    Why State Attorneys General Are Leading the Charge

    State attorneys general have become key players in tech regulation, especially when federal efforts stall. They have broad authority to enforce consumer protection laws, and they can act quickly.

    The bipartisan nature of this coalition is significant. It suggests that AI safety is not a partisan issue but a consumer protection concern that crosses party lines. This could put pressure on OpenAI to take the demands seriously, as ignoring a bipartisan group of AGs could lead to legal consequences in multiple states.

    The Technical Challenge: Can AI Be Sandboxed Effectively?

    From an engineering perspective, sandboxing is feasible but not trivial. AI systems that are designed to interact with the real world—via APIs, for example—need to be able to take actions. Restricting those actions can hamper functionality.

    However, the AGs are not asking for AI to be crippled; they’re asking for it to be contained. This is a reasonable expectation. For instance, an AI customer service bot should not be able to access internal HR databases. A sandbox can enforce that boundary.

    The real challenge lies in the fact that AI is probabilistic. It can be unpredictable, and even well-designed sandboxes can be bypassed if the AI is cleverly manipulated. But that doesn’t mean sandboxing is pointless; it’s a risk-reduction measure, not a silver bullet.

    What This Means for OpenAI and the Industry

    OpenAI has positioned itself as a safety-first company, but it has also been criticized for rolling out features—like memory, custom GPTs, and agentic tools—that expand the attack surface for misuse. This demand from the AGs could push OpenAI to adopt a more security-focused approach.

    It could also set a precedent for other states. If OpenAI complies with Iowa’s coalition, other AGs may make similar demands, leading to a patchwork of state-level regulations. This could be a headache for compliance, but it might also lead to a more standardized security framework if the demands are consistent.

    The Broader Debate: Innovation vs. Safety

    This situation highlights a tension that runs through all discussions of AI regulation: the balance between innovation and safety.

    Some argue that over-restriction could stifle the US’s competitive edge in the global AI race. Others contend that without safety measures, public trust will erode, ultimately slowing adoption.

    The AGs’ demand suggests a middle path: they are not asking for a moratorium on AI development, but for responsible deployment. Sandboxing is a way to have both—AI can still be powerful and useful, but it is contained to prevent harm.

    Looking Ahead: What Happens Next?

    The coalition’s demand is a signal, not a final verdict. OpenAI will need to respond, and that response could shape future interactions between tech companies and state regulators.

    If OpenAI agrees to the demands, it could set a new standard for transparency and security in the industry. If it resists, it may face legal challenges or reputation damage.

    Either way, this is a moment worth watching. It shows that the conversation about AI safety is moving from theoretical discussions to concrete regulatory actions.

    The Iowa AG’s coalition is asking OpenAI to do something that seems reasonable on its face: be transparent about security issues and keep AI systems contained. Whether OpenAI will comply remains to be seen, but this demand could be a pivotal moment in the push for responsible AI development. For consumers, it’s a reminder that the AI tools we use are powerful—and that those in power are starting to demand they be used safely.

    Summary

    • Iowa Attorney General Brenna Bird is leading a bipartisan coalition of state AGs demanding OpenAI transparency after an alleged AI breach.
    • The coalition asks for details on the breach’s scope, data accessed, and assurance that AI bots will be ‘sandboxed’ to prevent future incidents.
    • Sandboxing is a containment measure that restricts AI actions and data access, reducing risks like prompt injection.
    • This move reflects state AGs’ growing role in tech regulation, especially when federal action is lacking.
    • The outcome could set precedents for AI security standards and influence the innovation-versus-safety debate.

    FAQ

    Q: What is an ‘AI breach’?
    A: An AI breach occurs when an AI system acts outside its intended boundaries—for example, accessing data or systems it shouldn’t, or being tricked into performing unintended actions via prompt injection.

    Q: What does ‘sandboxing’ mean for AI?
    A: Sandboxing is a security practice where AI runs in an isolated environment with restricted permissions, limiting what it can access or do. It’s like putting the AI in a fenced-off area where it can’t wander into places it shouldn’t.

    Q: Why are state attorneys general involved?
    A: State AGs have consumer protection authority and can act when they see potential harm to citizens. They often step in when federal regulation is absent or slow.

    Q: Is sandboxing technically possible for advanced AI?
    A: Yes, it’s feasible, though challenging for AI that needs to interact with external systems. It’s a risk-reduction measure, not a perfect solution.

    Q: What could happen if OpenAI doesn’t comply?
    A: OpenAI could face legal action from individual states, reputational damage, and increased scrutiny from other regulators. Compliance could set a new industry standard.