Tag: privacy

  • Nitter and XCancel Receive Cease and Desist: What It Means for Privacy Tools

    Nitter and XCancel Receive Cease and Desist: What It Means for Privacy Tools

    In a move that has sent ripples through the privacy and open-source communities, Nitter a popular alternative frontend for X (formerly Twitter) and its companion service XCancel have reportedly received cease and desist notices. The news, first surfaced via a GitHub issue on the Nitter repository, quickly gained traction on Hacker News, where it sparked a heated debate about the future of such tools.

    For the uninitiated, Nitter allows users to browse public tweets without JavaScript, ads, or tracking, making it a favorite among privacy advocates and researchers. XCancel acts as a directory and redirector, ensuring users can always find a working Nitter instance. The legal pressure on these projects raises existential questions: Can open-source tools survive legal threats from tech giants? And what does this mean for your ability to access public data without surveillance?

    The Backstory: What Are Nitter and XCancel?

    Nitter is an open-source project that provides a lightweight, privacy-respecting interface to X/Twitter. Instead of loading the full Twitter web app, which is heavy on JavaScript and tracking pixels, Nitter serves a simple page with just the content: tweets, profiles, and search results. It does this by scraping X’s public endpoints without requiring login or exposing your IP address to X’s trackers.

    XCancel is a simple web service that maintains a list of active Nitter instances. When you visit XCancel, it automatically redirects you to a Nitter instance that is currently online, acting like a load balancer for the Nitter ecosystem. If one instance goes down, XCancel points you to another.

    Both tools have been around for years, surviving technical countermeasures from X—rate limiting, IP bans, and changes to API endpoints. But a cease and desist letter is a different beast entirely: it’s a legal threat, not a technical one.

    The Cease and Desist: What We Know

    The primary record of the cease and desist comes from a GitHub issue on the Nitter repository (zedeus/nitter/issues/1442). The issue presumably details the notice, though the exact wording is not public. XCancel’s website also appears to acknowledge the situation, though the specific notice is not captured in the research brief.

    The news exploded on Hacker News, with over 800 points and 600+ comments, indicating widespread concern. The community is speculating about who sent the notices—most assume X Corp., given Nitter’s direct competition with X’s business model—but no official confirmation exists yet.

    Why X Corp. Might Be Worried

    To understand X Corp.’s motivation, consider the business model. X generates revenue from ads, premium subscriptions, and data licensing. Nitter undermines all three by providing a free, ad-free, tracking-free view of public content. When users access X through Nitter, they aren’t seeing ads, aren’t being tracked, and aren’t paying for a subscription. If Nitter becomes widespread, X’s ad impressions and data collection take a hit.

    Moreover, Nitter bypasses rate limits that X imposes on unauthorized API access. This can lead to server strain and enables behaviors X wants to discourage, like mass data harvesting.

    The Legal Landscape: Can They Do That?

    A cease and desist letter is not a lawsuit; it’s a demand to stop certain activities, backed by the threat of legal action. The legal basis for X’s claim likely hinges on X’s Terms of Service, which explicitly prohibit scraping without permission. However, the enforceability of those terms against someone who isn’t a direct user is contested.

    A key precedent is hiQ Labs v. LinkedIn. In that case, the Ninth Circuit ruled that scraping publicly accessible data does not violate the Computer Fraud and Abuse Act (CFAA). That decision was a win for scrapers, but it was later vacated and settled, leaving the law ambiguous. Other cases, like Facebook v. Power Ventures, have gone the other way when scraping involved breached access barriers.

    Nitter operates in a gray area: it accesses public data, but it does so in a way that circumvents technical measures (like login walls) and violates X’s ToS. Whether that constitutes a legal violation remains unclear.

    The Open-Source Catch-22

    One of the most discussed aspects is the futility of sending a C&D to an open-source project. Nitter’s code is freely available on GitHub, and anyone can fork it. Even if the main repository is taken down, dozens of mirrors exist. The maintainer, zedeus, is based in Sweden, adding a layer of jurisdictional complexity to any legal action.

    For XCancel, the situation is similar. It’s a simple redirector; someone could replicate it in minutes. The C&D might force these specific projects to shut down, but the cat is already out of the bag. This raises the question: is this a genuine legal attempt, or more of a scare tactic? The latter is plausible, as the cost of defending a lawsuit—even a frivolous one—can crush a small open-source project. Many projects have folded under such pressure, not because they lost in court, but because they couldn’t afford to fight.

    Precedents in the Ecosystem

    Nitter and XCancel are not alone. Similar alternative frontends have faced legal pressure:

    • Invidious, an alternative YouTube frontend, has received takedown notices from Google.
    • Bibliogram, which did the same for Instagram, shut down partly due to legal threats.
    • Twitter API scrapers used in academic research have been sued or threatened by X Corp.

    These cases often end quietly, with the tool shutting down or going underground. But some, like Bright Data, have fought back and won. Bright Data, a web scraping company, successfully defended against X’s lawsuit, and the court dismissed X’s claims. This shows that scraping public data is not automatically illegal, but the legal waters are murky.

    What This Means for Users

    If you use Nitter or XCancel, the immediate impact may be minimal. Existing instances may continue to run, and new ones may pop up. But if the C&D leads to a lawsuit and the projects are shut down, you’ll lose a valuable tool for privacy-preserving access to X.

    More importantly, this is a signal of the ongoing battle over public data. Tech companies are increasingly locking down their platforms, and tools like Nitter push back against that trend. The outcome could set a precedent for how much control companies have over data that users post publicly.

    The Road Ahead

    The Nitter and XCancel teams have not yet announced their response. Options include:

    • Compliance: Shutting down as demanded, which would be a loss for the community.
    • Defiance: Continuing to operate, perhaps in a decentralized manner, risking a lawsuit.
    • Legal Defense: Crowdfunding to fight the C&D, as some projects have done.

    The community is already rallying, with calls to support the developers and potentially fund a legal defense. In the meantime, users can still access Nitter instances via various mirrors, and XCancel’s status page may provide updates.

    For now, the situation is a waiting game. But one thing is certain: the cat-and-mouse game between X Corp. and privacy tools is far from over.

    The cease and desist notices against Nitter and XCancel highlight the fragility of privacy-respecting tools in the face of corporate legal power. While the future of these specific projects is uncertain, the open-source ethos ensures that similar tools will continue to emerge. Whether they can survive legal challenges depends on the community’s willingness to support them—both financially and legally. As users, we should pay attention to this case, because it could set a precedent for how public data is accessed in the future.

    Summary

    • Nitter and XCancel have reportedly received cease and desist notices, likely from X Corp.
    • Nitter is an open-source, privacy-friendly frontend for X; XCancel redirects users to active Nitter instances.
    • X Corp. may be targeting them for bypassing ads, tracking, and rate limits, undermining its business model.
    • Legal precedent on scraping public data is ambiguous, but C&Ds can be effective as scare tactics due to legal costs.
    • Open-source projects can survive via forks, but the threat of lawsuits may still lead to shutdowns.

    FAQ

    Q: What is Nitter?
    A: Nitter is a free, open-source alternative frontend for X/Twitter that lets you view public tweets without JavaScript, ads, or tracking. It scrapes public data from X, so you can browse without exposing your IP to X’s trackers.

    Q: What is XCancel?
    A: XCancel is a web service that maintains a list of active Nitter instances and redirects you to a working one automatically. It acts as a load balancer for the Nitter network, ensuring you can always find an accessible instance.

    Q: Why would X Corp. send a cease and desist?
    A: X Corp. likely wants to protect its business model, which relies on ads, subscriptions, and data licensing. Nitter bypasses these revenue streams by providing a free, ad-free view of public content, and it scrapes data in ways that may violate X’s Terms of Service.

    Q: Can X Corp. legally force Nitter to shut down?
    A: Not automatically. A cease and desist is just a demand; only a court can order a shutdown. The legality of scraping public data is unclear, with precedent like hiQ v. LinkedIn suggesting it may be legal, but other cases have gone the other way. The cost of defending a lawsuit can be prohibitive, though, which is why many projects shut down.

    Q: What can I do to help?
    A: You can support the Nitter and XCancel developers, perhaps by donating to a legal defense fund if one is established. You can also continue to use Nitter instances and spread awareness about the importance of privacy-preserving tools.
  • The $1 Car Insurance Fee Funding Flock Cameras in Texas

    The $1 Car Insurance Fee Funding Flock Cameras in Texas

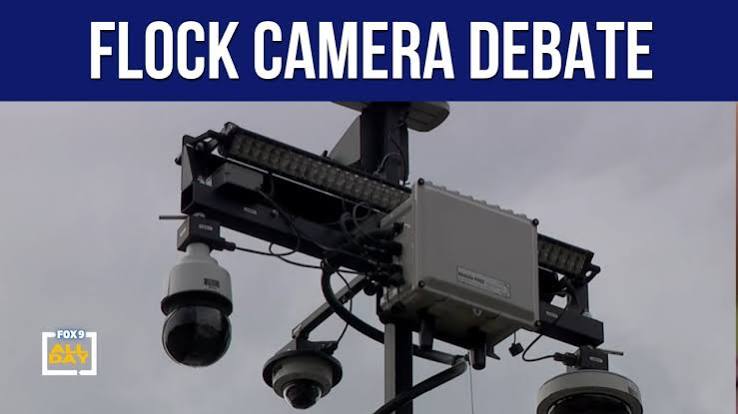
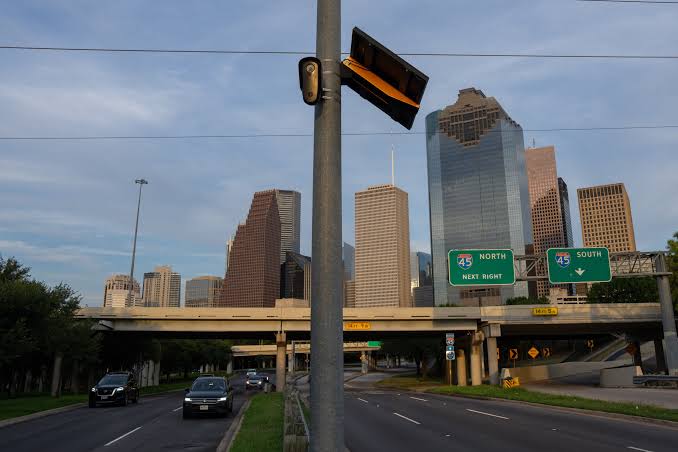
    If you drive a car in Texas, you’re likely paying a hidden $1 fee on your auto insurance policy. That dollar doesn’t go to the insurance company it funds the Motor Vehicle Crime Prevention Authority (MVCPA), a state agency created in 2001 to combat auto theft. But in recent years, the MVCPA has been using that money to buy Flock Safety cameras, automated license plate readers that are popping up on poles across the state.

    These cameras aren’t just watching for stolen cars. They’re part of a growing network of surveillance that records every vehicle that passes by whether it’s involved in a crime or not. And most drivers have no idea their insurance premiums are footing the bill. This article explains how that $1 fee works, how it got redirected from fighting auto theft to funding a private surveillance company, and what it means for your privacy.

    How the $1 Fee Works

    Back in 2001, the Texas Legislature created the MVCPA to tackle a specific problem: auto theft. To fund it, they added a $1 surcharge to every motor vehicle liability insurance policy written in the state. If you buy car insurance in Texas, you pay this fee—it’s listed as a line item on your policy, often bundled into the premium so you don’t notice it.

    The MVCPA then distributes this money as grants to local law enforcement agencies. For years, those grants went to auto theft task forces, bait vehicles, and investigative units. The idea was straightforward: use a small fee on every driver to fund efforts to catch car thieves.

    But over time, the agency’s mandate broadened. The Legislature expanded the definition of “motor vehicle crimes” to include things like hit-and-runs and theft from vehicles. That change opened the door for funding technology like license plate readers, which can help solve a wide range of crimes beyond just auto theft.

    The $1 fee on your car insurance was meant to fight auto theft—and it still does, in part. But it’s also become a funding stream for a private surveillance company with cameras on thousands of poles across Texas. Whether that’s a good use of your dollar depends on how you weigh public safety against privacy. If you’re uncomfortable with the trade-off, ask your state representative why a fee for fighting auto theft is now paying for mass surveillance—and whether that’s what you signed up for when you bought your policy.

    Summary

    • A $1 fee on every car insurance policy in Texas funds the Motor Vehicle Crime Prevention Authority (MVCPA), a state agency created in 2001 to fight auto theft.
    • The MVCPA now uses those funds to give grants to police departments to buy Flock Safety cameras—automated license plate readers that record every passing vehicle.
    • Texas has become one of Flock’s largest markets, with hundreds of agencies using the cameras.
    • Critics argue this is a form of warrantless mass surveillance, since the cameras capture everyone’s movements, not just suspects’.
    • Supporters say the cameras help solve crimes like car theft and hit-and-runs, and that the fee is already in place, so it’s a natural evolution of the MVCPA’s mission.

    FAQ

    Q: How do I know if I’m paying the $1 fee?
    A: Check your auto insurance policy document—it should list a $1 surcharge for “Motor Vehicle Crime Prevention Authority” or similar. It’s often bundled into your total premium, so you may not see it unless you read the fine print.

    Q: What exactly do Flock cameras do?
    A: Flock cameras are solar-powered, cellular-connected devices that capture license plates and vehicle characteristics (make, model, color, and sometimes roof racks or bumper stickers). They take photos of every vehicle that passes and store the data for 30 days by default.

    Q: Can the police access my data without a warrant?
    A: Flock cameras capture data on all vehicles, not just suspects. Law enforcement can search that data for specific plates or vehicle descriptions. In many cases, they do this without a warrant, raising privacy concerns.

    Q: Why are these cameras controversial?
    A: Privacy advocates argue that ALPRs create a searchable database of everyone’s movements, which could be used for purposes beyond crime-solving, such as tracking people at protests or reproductive health clinics. There’s also concern about equitable deployment—cameras often go in affluent suburbs where residents can afford the subscription.

    Q: Is the $1 fee a new tax?
    A: No, the fee has existed since the early 2000s. What’s changed is how the money is allocated. Instead of only funding auto theft task forces, the MVCPA now also funds ALPR networks, which is a significant departure from its original mission.

  • Outcome-Based Auctions: When Advertisers Pay Only for Real-Life Results

    Outcome-Based Auctions: When Advertisers Pay Only for Real-Life Results

    Imagine a world where you only pay for a car advertisement if the viewer actually buys the car not just clicks the ad or visits the showroom. That’s the promise of outcome-based auctions (OBAs), a new advertising model that’s shifting the focus from keyword bids to delivering life outcomes. Instead of paying for clicks or impressions, advertisers now bid on the value of a completed job application, a booked doctor’s appointment, a signed mortgage, or a finished online course. This article explains how OBAs work, why they’ve emerged now, and what they mean for advertisers and platforms.

    The Evolution of Ad Auctions: From Impressions to Outcomes

    To understand outcome-based auctions, let’s look at how online advertising has evolved. In the 1990s, advertisers paid for impressions (CPM) they paid just to have their ad seen, regardless of whether anyone clicked or cared. Then, in the 2000s, Google AdWords popularized pay-per-click (CPC), where you paid only when someone clicked your ad. This was a big step because it tied cost to user interest.

    In the 2010s, advertisers started optimizing for conversions actions like purchases or sign-ups—using tracking pixels. Bidding became algorithmic with Smart Bidding and target CPA (cost-per-acquisition). But these conversions were still website events. Now, with outcome-based auctions, the focus shifts even further: to real-world outcomes that happen offline or later in time, like a loan approval, a completed degree, or a patient actually showing up for surgery.

    How Outcome-Based Auctions Work

    In an outcome-based auction, the advertiser specifies a desired outcome say, a booked appointment and sets a target cost per acquisition (tCPA) or target return on ad spend (tROAS). The ad platform uses machine learning to predict the probability that a given user will complete that outcome. The auction then happens in real time, but the payment is triggered only when the outcome is achieved (or when the platform’s algorithm decides it’s highly likely).

    For example, consider a dental clinic that wants to fill its appointment schedule. With traditional CPC, they’d bid on keywords like “dentist near me” and pay for every click, even if the visitor never books. With an outcome-based auction, they’d set a tCPA of, say, $50 per booked appointment. The platform then shows their ads to users most likely to book, and the clinic pays only when an appointment is actually made.

    This model relies heavily on machine learning. The platform’s algorithms analyze vast amounts of data user behavior, device, time of day, past conversions to predict outcome probabilities. The advertiser doesn’t need to manage keywords or placements; they just set their target and let the system optimize.

    Why Now? The Perfect Storm of Privacy, AI, and Advertiser Fatigue

    Several factors have converged to make outcome-based auctions the new default. First, privacy regulations like GDPR and CCPA, along with the phasing out of third-party cookies, have made it harder to track individual users. Outcome-based models depend less on identifying specific users and more on aggregate prediction, making them more privacy-resilient.

    Second, machine learning has matured dramatically. Deep learning models can now predict long-term outcomes from sparse, noisy signals—like a user’s browsing history or app usage—with impressive accuracy.

    Third, advertisers are tired of vanity metrics. Clicks and impressions don’t correlate well with business results. CFOs demand ROI tied to revenue or lifetime value, not just traffic. Outcome-based auctions align spend directly with business results, eliminating wasted spend on clicks that don’t convert.

    Finally, brands are collecting their own first-party data—CRM data, offline sales, app usage—and feeding it back into ad platforms. This creates a closed loop where outcomes can be measured and optimized.

    Who’s Leading the Charge?

    Google, Meta, and Amazon are all moving aggressively toward outcome-based bidding. Google’s Performance Max campaigns automatically allocate budget across channels to optimize for conversions, which can be defined as outcomes like purchases or lead forms. Meta offers Advantage+ Shopping Campaigns and Conversions API, which feed offline and online outcome data back into the auction. Amazon uses Cost-per-Purchase (CPP) bidding for sponsored products, where advertisers pay only when a purchase occurs.

    Retail media networks like Walmart Connect, Target, and Kroger are also building closed-loop measurement systems where the outcome is a verified in-store or online purchase. Emerging platforms like TikTok and Pinterest are adopting outcome-based bidding as their default as well.

    The scale is significant: over 80% of advertisers now use automated bidding strategies (which are outcome-optimized) for at least some campaigns.

    The Upside for Advertisers

    For advertisers, the biggest advantage is alignment with business results. You’re no longer paying for clicks that don’t convert; you’re paying for outcomes that matter. This reduces wasted spend and simplifies campaign management—no more manual bid adjustments or keyword research.

    Outcome-based auctions also level the playing field. Smaller advertisers can compete with large brands by focusing on outcome efficiency rather than outbidding on keywords. If your conversion rate is better, you can win auctions at a lower cost.

    The Caveats and Challenges

    But there are downsides. The “black box” problem is real: advertisers often can’t see or control which keywords, placements, or audiences trigger their ads. You’re trusting the platform’s algorithm to make the right calls. If the algorithm is wrong, you might waste budget.

    Data quality is critical. Outcomes must be accurately tracked and fed back to the platform. If your tracking is broken, the algorithm will optimize for the wrong things. For example, if a conversion is counted when someone just visits a thank-you page rather than actually completing a purchase, you’ll get poor results.

    Long sales cycles pose another challenge. For high-consideration outcomes like buying a house, the delay between ad exposure and outcome makes attribution difficult. The platform may not be able to connect the dots, leading to under-optimization.

    The Platform Perspective: Risk and Reward

    For platforms, outcome-based auctions offer a way to increase revenue. They can charge a premium for “guaranteed” outcomes and algorithmic bidding increases competition. But they also bear more risk—if the outcome doesn’t happen, they don’t get paid. Platforms mitigate this by using sophisticated prediction models to ensure they only charge when the outcome is highly likely.

    The Future: Moving Beyond Website Conversions

    The next step is moving beyond website conversions to real-world outcomes. For example, a university might bid on “enrolled student” rather than “application submitted.” A hospital might bid on “patient completed treatment” rather than “appointment scheduled.” This requires integrating offline data, which is already happening through platforms like Google’s offline conversion tracking and Amazon’s attribution tools.

    What Advertisers Should Do Now

    If you’re an advertiser, the time to embrace outcome-based auctions is now. Start by defining the outcomes that matter most to your business—not just clicks or conversions, but actual business results. Ensure your tracking is robust, using first-party data and conversion APIs to feed accurate outcome data to the platforms. Then, test outcome-based bidding strategies like tCPA or tROAS, and be prepared to give up some control in exchange for efficiency.

    As privacy regulations tighten and machine learning improves, outcome-based auctions will likely become the standard. Advertisers who adapt early will gain a competitive advantage; those who cling to outdated models may find themselves left behind.

    Outcome-based auctions represent a fundamental shift in how advertising is bought and sold. By tying payment to real-world outcomes, they align advertising spend with business results, reduce waste, and leverage AI to predict and deliver value. While challenges like data quality and loss of control remain, the trend is clear: the future of advertising is outcomes, not clicks. Advertisers who embrace this model now will be better positioned to thrive in a privacy-first, AI-driven world.

    Summary

    • Outcome-based auctions (OBAs) tie payment to measurable life outcomes (e.g., booked appointments, completed purchases) rather than clicks or impressions.
    • OBAs rely on machine learning to predict outcome probabilities, with bidding expressed as target CPA or ROAS.
    • The shift is driven by privacy regulations, cookie deprecation, AI maturity, and advertiser demand for ROI.
    • Major platforms like Google, Meta, and Amazon have adopted outcome-based bidding as default.
    • Advertisers benefit from alignment with business results and reduced waste, but face challenges like the “black box” problem and data quality requirements.

    FAQ

    Q: What is an outcome-based auction?
    A: An outcome-based auction is an advertising model where the auction and payment are tied to a specific, measurable lifecycle event—like a completed purchase, a booked appointment, or a signed contract—rather than an intermediate signal like a click or impression. Advertisers bid on the value of that outcome, and the platform uses machine learning to predict and optimize for it.

    Q: How is an outcome-based auction different from cost-per-click (CPC) or cost-per-acquisition (CPA)?
    A: With CPC, you pay for each click regardless of whether it leads to a sale. With CPA, you pay for a conversion event that happens on your website, like a form submission. With OBA, the outcome can be an offline or delayed event, such as a loan approval or a patient showing up for surgery, and you only pay when that outcome occurs.

    Q: What are some examples of outcome-based bidding?
    A: Google’s Performance Max, Meta’s Advantage+ Shopping Campaigns, and Amazon’s Cost-per-Purchase bidding are all examples. For instance, a dental clinic could use tCPA bidding to pay only when a patient books an appointment, not just when they click an ad.

    Q: What are the main benefits for advertisers?
    A: The main benefits are aligning ad spend with business results, reducing wasted spend on non-converting clicks, simplifying campaign management, and enabling smaller advertisers to compete based on efficiency rather than budget size.

    Q: What are the challenges of outcome-based auctions?
    A: Challenges include the loss of control over keywords and placements (the “black box” problem), the need for accurate outcome tracking and data quality, and difficulties with long sales cycles where attribution becomes harder.

  • 5 Privacy Hacks That Actually Work (Without Overhauling Your Digital Life)

    5 Privacy Hacks That Actually Work (Without Overhauling Your Digital Life)

    You don’t need to disappear from the internet to protect your data. In fact, the most effective privacy measures are often the least dramatic: a password manager, a second verification step, a browser that blocks trackers, a VPN on public Wi-Fi, and a quick review of which apps can see your location. These aren’t exotic tools for spies—they’re practical habits that take minutes to set up and save you from the most common ways data gets stolen or sold.

    Start with the basics: your passwords are the weakest link

    The average person has between 100 and 200 online accounts, yet most people reuse the same handful of passwords. That’s a goldmine for hackers. The 2023 Verizon Data Breach Investigations Report found that 74% of breaches involve the human element, often through stolen or weak credentials.

    The fix is simple: use a password manager. It generates a unique, random password for every site and stores them in an encrypted vault. You only need to remember one master password. Most managers also alert you if a site you use has been breached, so you can change that password before someone exploits it.

    If you’re skeptical, think of it this way: a password manager is like having a locksmith who changes the lock on every door in your building and gives you a single master key. You wouldn’t trust the same key for your front door, your car, and your safety deposit box—so why do the same with your bank, email, and social media?

    Turn on two-factor authentication (2FA) everywhere that matters

    A password alone is no longer enough. Two-factor authentication (2FA) adds a second check—usually a code from an app on your phone or a hardware key—so even if someone steals your password, they can’t get in.

    SMS-based 2FA is better than nothing, but it’s vulnerable to SIM-swapping attacks. Instead, use an authenticator app like Google Authenticator or Authy, or a hardware key like a YubiKey. These are far harder to intercept.

    Still, adoption is low. A 2022 survey by Google found that only about 30% of users had enabled 2FA. That’s a small effort with a huge payoff: Microsoft reports that 2FA blocks 99.9% of automated attacks on your account.

    Start with your most sensitive accounts: email, banking, and social media. Once those are protected, move on to the rest.

    Use a VPN, but only for the right reasons

    A VPN (virtual private network) encrypts your internet traffic and routes it through a server in another location, masking your IP address. That’s essential on public Wi-Fi—like at a coffee shop or airport—where attackers can intercept unencrypted data.

    But a VPN is not a magic cloak of anonymity. The VPN provider can still see your traffic, and it won’t protect you from phishing or malware. Choose a reputable, no-logs VPN (one that doesn’t record your activity) and use it whenever you’re on an untrusted network. At home, it’s less critical, unless you want to hide your browsing from your ISP.

    A common misconception is that a VPN makes you invisible. It doesn’t. It just makes it harder for websites and network snoops to see what you’re doing. Think of it as a locked car on a highway—it’s not invisible, but it’s much harder to break into than an open one.

    Lock down your browser and social media settings

    Your browser and social media accounts are leaky faucets. They’re designed to collect as much data as possible about you—your interests, your location, your friends, your buying habits. The good news is that you can turn off most of the taps.

    Start with your browser. Install an ad blocker like uBlock Origin and a tracker blocker like Privacy Badger. Use a browser with built-in tracking protection, like Firefox or Brave. Switch your default search engine to DuckDuckGo, which doesn’t track your searches.

    On social media, review your privacy settings. On Facebook, for example, you can limit who sees your posts, disable facial recognition, and stop advertisers from using your data for targeted ads. On your phone, check which apps have access to your location, camera, and microphone. If a flashlight app needs your location, something’s wrong. Revoke permissions you don’t need.

    Remember: incognito mode is not the privacy shield many people think it is. It only prevents your browser from saving history and cookies on your device. Your ISP, employer, and the websites themselves can still see your activity. To limit that, you need the browser settings and VPN described above.

    Use encrypted messaging for sensitive conversations

    Most people text or use WhatsApp or Facebook Messenger. Those aren’t all end-to-end encrypted by default (WhatsApp is, but Messenger isn’t unless you turn on secret conversations). For truly private chats, use an app that encrypts messages from sender to receiver—and nothing else.

    Signal is the gold standard. It’s free, open-source, and used by security experts and journalists. Its encryption is so strong that the app’s own developers can’t read your messages. WhatsApp uses the same encryption protocol, but it’s owned by Facebook (Meta), which collects metadata about your conversations.

    For most people, the threat isn’t a government spy—it’s a company compiling a profile of you to sell ads, or a cybercriminal trying to scam you. Encrypted messaging ensures that even if someone intercepts your messages, they can’t read them.

    A practical tip: encourage your friends and family to use Signal for anything you wouldn’t want posted on a billboard. It’s a small shift in habit that makes a big difference for your collective privacy.

    Review your app permissions regularly

    Apps are notorious for asking for more permissions than they need. That’s not an accident—it’s a data collection strategy. A simple puzzle game doesn’t need access to your contacts, and a weather app doesn’t need your microphone.

    On your phone, go to settings and review each app’s permissions. On iPhone, go to Privacy & Security; on Android, go to Privacy. Turn off anything that isn’t essential. For example, you might allow your maps app to use your location only while you’re using it, not in the background. And if an app asks for location “always,” ask yourself why.

    This is a habit, not a one-time fix. New apps are installed and permissions change. Set a reminder every few months to do a quick audit. It takes about 10 minutes and can dramatically reduce the amount of data you leak.

    Also, consider freezing your credit. This is a US-specific step, but it’s one of the most powerful ways to prevent identity theft. A credit freeze blocks new accounts from being opened in your name. You’ll need to lift it temporarily if you apply for a loan or credit card, but it’s a small price for peace of mind.

    The bottom line: privacy is a practice, not a product

    These five hacks won’t make you anonymous, but they’ll make you a much harder target. The goal is to reduce your exposure to the most common threats: data breaches, identity theft, and surveillance capitalism. Start with the password manager and 2FA—that’s the foundation. Then add a VPN for public Wi-Fi, tweak your browser and social settings, and switch to encrypted messaging for sensitive chats.

    Privacy isn’t about being paranoid. It’s about being intentional with your data. You wouldn’t hand your house keys to a stranger; don’t hand over your digital keys without a thought.

    Protecting your data online doesn’t require a complete digital detox or a degree in cybersecurity. It starts with a few deliberate choices: strong, unique passwords; two-factor authentication; a VPN when you’re on public Wi-Fi; tighter browser and social media settings; and encrypted messaging for private conversations. These steps are simple, effective, and—most importantly—habit-forming. The more you practice them, the more natural they become. And in a world where data is the new currency, that’s a habit worth building.

    Summary

    • Use a password manager to generate and store unique passwords for every account, reducing the risk of credential stuffing attacks.
    • Enable two-factor authentication (2FA) on your most sensitive accounts, preferring app-based or hardware keys over SMS.
    • Use a VPN on public Wi-Fi to encrypt your traffic and hide your IP address, but remember it’s not a substitute for caution.
    • Adjust your browser and social media privacy settings to block trackers, disable targeted ads, and limit data sharing.
    • Review app permissions regularly and use encrypted messaging apps like Signal for sensitive conversations.

    FAQ

    Q: Is incognito mode private?
    A: No. Incognito mode only prevents your browser from saving your history and cookies on your device. Your ISP, employer, and the websites you visit can still see your activity.

    Q: Can a VPN make me completely anonymous?
    A: No. A VPN hides your IP address from websites, but the VPN provider can still see your traffic. Choose a no-logs VPN and use it for privacy on public Wi-Fi, but don’t rely on it for absolute anonymity.

    Q: What’s the best encrypted messaging app?
    A: Signal is widely considered the gold standard for end-to-end encryption. It’s free, open-source, and doesn’t collect metadata. WhatsApp uses similar encryption but is owned by Meta, which collects metadata.

    Q: How often should I review my app permissions?
    A: At least every few months. New apps are installed, and existing apps may update their permissions. A quick audit takes about 10 minutes and can significantly reduce data leakage.

    Q: Will these hacks protect me from all cyber threats?
    A: No. They protect against common threats like password theft, data breaches, and some tracking. They won’t protect against malware or phishing, so always be cautious about clicking links and downloading files.

  • Winona’s Flock Cameras Stolen: What It Means for Surveillance and Safety

    Winona’s Flock Cameras Stolen: What It Means for Surveillance and Safety

    In a small Minnesota city, something unusual happened: every single automated license plate reader camera owned by the police was cut down and stolen in one coordinated operation. The Winona Police Department lost its entire fleet of Flock Safety cameras overnight, leaving investigators without a tool they had come to rely on. This incident raises important questions about the role of surveillance technology in small towns, the vulnerabilities of such systems, and what happens when they are taken away.

    For residents of Winona, the theft is both puzzling and concerning. Were the cameras targeted by criminals trying to avoid detection? Or was this an act of protest against mass surveillance? The answer is not yet clear, but the event highlights a growing tension between public safety and privacy in communities across the United States.

    What Are Flock Cameras?

    Flock cameras are automated license plate readers (ALPRs) made by a private company called Flock Safety. They are small, solar-powered devices that can be attached to existing poles, like streetlights or utility poles. Each camera takes photos of every license plate that passes by and uploads the data to a cloud-based system. Police can then search for specific plates—for example, those linked to a stolen car or an AMBER Alert—and get a list of locations where that vehicle has been seen.

    Unlike traditional surveillance cameras that record video, Flock cameras only capture still images of license plates and vehicle characteristics (like make, color, and unique features). They do not record people’s faces or live video feeds. The idea is to provide investigators with leads, not to monitor people in real time.

    The Theft: A Coordinated Effort

    On August 4, 2026, Winona Police discovered that all of their Flock cameras had been cut down from their poles and stolen. This was not a random act of vandalism—it required planning, tools, and likely multiple people working together. To remove a camera, someone would need to climb up to the pole, cut the mounting bracket (possibly with an angle grinder or bolt cutters), and then lower the device down without being noticed. Doing this for every camera in the city suggests the thieves knew exactly where each one was located and had a way to move quickly.

    Authorities described the theft as “coordinated,” meaning they believe it was a deliberate operation, not a spontaneous crime. As of the initial report, no suspects had been identified, and the investigation was ongoing.

    Why Would Someone Steal All the Cameras?

    There are several possible motivations, and the truth may be a combination of them:

    • Criminal activity: Criminals who want to avoid being tracked might steal the cameras to reduce the chance of being caught. If the cameras are gone, police lose a valuable tool for solving property crimes and identifying suspects.
    • Anti-surveillance activism: Some people oppose automated license plate readers because they see them as an invasion of privacy. While most activists would not endorse theft, a few might resort to direct action to remove what they see as an intrusive surveillance system.
    • Profit: Flock cameras are not cheap—they cost around $2,000 to $3,000 each. They could be resold on the black market or stripped for parts.
    • Personal grudge: Someone with a vendetta against the police department might have targeted the cameras as a way to cause disruption.

    The Impact on Winona Police

    For a department in a city of about 27,000 people, losing all Flock cameras is a significant setback. These cameras were likely used to solve crimes like car thefts, burglaries, and even more serious offenses. Without them, investigators will have to rely on traditional methods, such as witness interviews and physical evidence, which can be slower and less effective.

    The financial cost is also a concern. Replacing the cameras could cost tens of thousands of dollars, money that might have to come from the city’s budget or grants. This could mean fewer resources for other public safety needs.

    The Privacy Debate

    This incident also brings up the ongoing debate about surveillance technology. Supporters of Flock cameras argue that they help solve crimes and make communities safer. They point to cases where ALPRs led to arrests or helped find missing persons. Opponents, however, worry about the potential for abuse. They ask: Who gets to access the data? How long is it stored? Can it be used to track innocent people?

    In Winona, the theft might actually fuel both sides. Police might say, “The fact that criminals stole the cameras proves they are effective—criminals want them gone.” Privacy advocates might respond, “This shows that surveillance infrastructure is vulnerable and can be used against the community.”

    What Happens to the Data?

    One question that often comes up is: What about the data already collected? Flock cameras typically store data in the cloud, not on the device itself. So even though the cameras are gone, the data they collected before the theft is likely still available to police. That means the thieves did not erase the past records—they only stopped future collection.

    This is an important point because it means the theft does not erase the surveillance that already occurred. It only prevents new data from being gathered.

    The Broader Implications

    This incident is not just about Winona. It highlights a vulnerability in how surveillance systems are deployed. Many cities and towns have installed Flock cameras without thinking much about their physical security. If a determined group can steal an entire fleet in one night, what does that say about the resilience of such systems?

    It also raises questions about the role of private companies in public safety. Flock Safety is a for-profit company that sells its cameras to police departments. When a camera is stolen, does the company offer a discount for replacements? Do they provide insurance? These are practical concerns that other departments might now consider.

    Looking Ahead

    As the investigation continues, Winona will have to decide whether to replace the cameras. Some residents may push for their return, citing public safety. Others may see this as an opportunity to reconsider whether such surveillance is necessary. The city council might hold public meetings to discuss the issue.

    For now, the cameras are gone, and the community is left to grapple with what that means. The theft was a bold move, but its consequences are still unfolding.

    The theft of Winona’s Flock cameras is a striking example of how surveillance technology can be both a tool for safety and a target for those who oppose it. While the investigation continues, the incident forces a conversation about privacy, security, and the lengths some will go to avoid being watched. Whether Winona rebuilds its camera network or rethinks its approach, this event will likely be a case study for other communities facing similar decisions.

    Summary

    • All of Winona Police Department’s Flock license plate reader cameras were stolen in a coordinated theft on August 4, 2026.
    • The cameras were cut down from their poles, indicating a planned operation by individuals with knowledge of their locations.
    • Motivations could include criminal avoidance, anti-surveillance activism, profit, or a personal grudge.
    • The theft impacts police investigative capabilities and carries significant replacement costs.
    • The incident highlights vulnerabilities in physical security of surveillance systems and sparks debate about privacy vs. safety.

    FAQ

    Q: What are Flock cameras?
    A: Flock cameras are automated license plate readers made by Flock Safety. They capture images of license plates and vehicle details, which police can search to help solve crimes.

    Q: Why were all the cameras stolen?
    A: The exact motive is unknown, but possibilities include criminals wanting to avoid detection, anti-surveillance activists, thieves looking to sell the hardware, or someone with a grudge against the police.

    Q: Will the stolen cameras affect police work?
    A: Yes, the loss of the cameras means police lose a tool for identifying suspects and solving crimes. They will have to rely on traditional investigative methods.

    Q: Is the data from the cameras lost?
    A: No, the data is stored in the cloud, not on the cameras themselves. So the data collected before the theft is still available to police.

    Q: What happens next?
    A: The police are investigating the theft. The city will need to decide whether to replace the cameras, which could be costly. The incident may also prompt public discussions about surveillance in Winona.

  • ICE Collected Nearly 1 Million DNA Samples Last Year—Including from Young Children

    ICE Collected Nearly 1 Million DNA Samples Last Year—Including from Young Children

    In the past year, U.S. Immigration and Customs Enforcement (ICE) collected DNA samples from nearly one million people, a staggering number that includes young children. These samples are not stored in a medical database; they are uploaded to the FBI’s Combined DNA Index System (CODIS), a national database designed for criminal justice. This practice, authorized by laws passed in 2005 and 2013, raises profound questions about privacy, civil liberties, and the treatment of immigrants and children.

    For many, the idea that a child’s DNA could be in a criminal database is unsettling. It blurs the line between civil immigration enforcement and criminal justice, and it happens without a conviction—or even a charge. Understanding how we got here, what the law allows, and what it means for individuals and families is essential for anyone concerned about privacy and government power.

    The Scale of DNA Collection

    In fiscal year 2024, ICE collected DNA from approximately 1 million people. This is a dramatic increase from previous years, driven by higher border encounters and more streamlined collection processes. The samples are taken via buccal swabs—a simple cheek swab—during booking or processing at detention facilities. This includes not only adults but also children, some as young as infants, who are detained or processed through immigration channels.

    The Legal Framework

    The collection is not a secret operation. It is authorized by two key laws:

    • The DNA Fingerprint Act of 2005: This law required federal agencies to collect DNA from all persons arrested, facing charges, or convicted. It was a response to the growing use of DNA in solving crimes.
    • The Violence Against Women Reauthorization Act of 2013: This extended DNA collection to individuals detained under immigration laws. This effectively made ICE a major collector of DNA, as it processes hundreds of thousands of detainees each year.

    These laws were designed to help law enforcement solve crimes and identify repeat offenders. However, they have been applied to civil immigration detainees—people who have not been charged with any crime, but are simply in the country without legal status or seeking asylum.

    What Is CODIS?

    The Combined DNA Index System (CODIS) is the FBI’s national DNA database. It was originally created to store DNA profiles of convicted offenders, arrestees, and forensic evidence from crime scenes. Law enforcement uses it to match DNA from crime scenes to individuals, a process called a “cold hit.” Once a profile is in CODIS, it remains there indefinitely, even if the person is never charged or is fully exonerated.

    For immigration detainees, having DNA in CODIS means that if their DNA matches evidence from a crime scene—even one they had nothing to do with—they could become a suspect. This is a significant privacy concern, as it treats non-criminals as potential criminals.

    The Inclusion of Children

    One of the most controversial aspects is the collection of DNA from children. In immigration detention, children are often processed with their families or as unaccompanied minors. They are swabbed just like adults. Children cannot consent to this, and their parents may not have a choice. The DNA is stored in CODIS, where it can be used for criminal investigations.

    This raises serious ethical questions. Children are not criminals, and they are not being charged with anything. Yet their genetic information is being added to a criminal database. This could have lifelong implications, as DNA is permanent and cannot be changed.

    Privacy and Civil Liberties Concerns

    Civil liberties advocates argue that collecting DNA from people who have not been convicted of a crime violates the Fourth Amendment, which protects against unreasonable searches and seizures. They also point out that the presumption of innocence is undermined when the government collects genetic data from people who are merely detained, not convicted.

    Immigrant rights groups see this as a form of surveillance that stigmatizes immigrant communities. It may deter people from seeking asylum or legal status, for fear that their DNA will be used against them.

    Legal scholars debate whether the “arrest” standard in the DNA Fingerprint Act applies to civil immigration detention. Some argue that the law’s language is being stretched beyond its original intent, which was to collect DNA from criminals, not from people in civil proceedings.

    The Tech and Data Ethics Angle

    The scale of data collection—1 million profiles per year—raises concerns about database security and potential misuse. Genetic data is highly sensitive and personal. If CODIS were breached, the information could be misused. Additionally, once a profile is in CODIS, it is very difficult to remove, even if the person is released or deported.

    There is also the question of informed consent. In many cases, detainees may not fully understand what is happening when they are swabbed. They may be told it is routine, but they may not realize that their DNA will be stored in a criminal database indefinitely.

    Common Misunderstandings

    • “DNA collection means you have a criminal record”: Not true. CODIS contains profiles of arrestees and detainees, not just convicts. A person can be fully exonerated or never charged, yet their DNA remains.
    • “ICE is doing this secretly”: The practice is authorized by law and has been reported on for years, but the scale (1 million) is new and may surprise people. It is not covert, but it is under-publicized.
    • “Children are being swabbed at school”: No. The collection happens in immigration detention and processing facilities, not in public settings. However, children in ICE custody are indeed subject to it.
    • “DNA is only used for identification”: CODIS profiles are used for forensic matching; they can link a person to a crime scene, even if they are innocent.

    The collection of nearly 1 million DNA samples by ICE, including from young children, is a significant expansion of government surveillance. While it is authorized by law, it raises serious privacy and civil liberties concerns. As genetic data becomes more central to law enforcement, it is crucial to have a public conversation about the balance between public safety and individual rights. For now, the DNA of immigrants and their children is being stored in a criminal database, with little oversight and few options for removal.

    Summary

    • ICE collected DNA from nearly 1 million people in the past year, including children, and uploaded it to the FBI’s CODIS database.
    • The collection is authorized by the DNA Fingerprint Act of 2005 and the Violence Against Women Reauthorization Act of 2013.
    • DNA is collected via buccal swabs from civil immigration detainees, not just criminals, raising privacy concerns.
    • Children in immigration custody are swabbed, and their DNA is stored indefinitely in a criminal database.
    • Critics argue this violates the Fourth Amendment and undermines the presumption of innocence, while supporters see it as a public safety tool.

    FAQ

    Q: Is it legal for ICE to collect DNA from children?
    A: Yes, under current law. The DNA Fingerprint Act of 2005 and the Violence Against Women Reauthorization Act of 2013 authorize DNA collection from all individuals detained by federal authorities, including immigration detainees and minors in custody.

    Q: Can parents refuse to have their child’s DNA collected?
    A: In practice, refusal is not an option. DNA collection is mandatory for all detainees, and refusal could lead to additional legal consequences or delays in processing.

    Q: What happens to the DNA after it is collected?
    A: The DNA profile is uploaded to CODIS, the FBI’s national DNA database. It is used for forensic matching in criminal investigations and remains in the database indefinitely, even if the person is released or deported.

    Q: Does having DNA in CODIS mean you are a criminal?
    A: No. CODIS contains profiles of arrestees and detainees, not just convicted criminals. Many people in CODIS have never been charged with a crime.

    Q: Can a person request to have their DNA removed from CODIS?
    A: It is very difficult. There is no standard process for removal, and once a profile is in CODIS, it is typically kept permanently. Some legal challenges have been made, but success is rare.

  • South Africa’s Privacy Law Is Here, but the Vulnerable Are Being Left Behind

    South Africa’s Privacy Law Is Here, but the Vulnerable Are Being Left Behind


    When South Africa’s Protection of Personal Information Act (POPIA) came into full force in July 2021, it was hailed as a landmark moment for privacy rights. Modeled on Europe’s GDPR, the law promised to give citizens control over their personal data and hold organizations accountable for misuse. But for millions of South Africans—those in townships, informal settlements, and rural areas—the promise of privacy remains distant.

    POPIA is a sophisticated legal framework, but its benefits are unevenly distributed. Vulnerable populations, including low-income communities, survivors of gender-based violence, migrants, and informal workers, often lack the digital literacy, resources, and bargaining power to exercise their rights. Meanwhile, they are the most likely to have their data exploited in exchange for essential services like social grants, healthcare, and even electricity. This article explores why South Africa’s privacy evolution is leaving the most vulnerable behind—and what can be done to bridge the gap.

    The Legal Framework: A Strong Start, but Gaps Remain

    POPIA, enacted in 2013 and fully operational since 1 July 2021, establishes eight conditions for lawful data processing, including accountability, purpose specification, and security safeguards. It also provides special protection for sensitive data like health, race, and sexual orientation. The Information Regulator can impose fines up to R10 million and even prison sentences for serious breaches.

    However, the law’s effectiveness depends on enforcement and awareness. While the Regulator has issued enforcement notices—including against a major credit bureau after a 2022 breach—many violations go unreported, especially in informal sectors where data handling is unregulated.

    The Digital Divide: Privacy for the Privileged

    Approximately 72% of South Africans have internet access, but this masks a stark divide. Urban, affluent users enjoy high-speed connectivity, while rural and low-income users rely on expensive prepaid mobile data. Many vulnerable individuals access the internet through shared devices, public Wi-Fi, or community internet cafes—making it nearly impossible to maintain private, secure sessions.

    Digital literacy is another barrier. Many users do not understand what data is being collected, by whom, or how to exercise their rights under POPIA. For example, a domestic worker using a smartphone to receive payments may unknowingly consent to data sharing by an app, without any comprehension of the implications.

    The Data-for-Services Economy: No Choice but to Share

    For vulnerable South Africans, sharing personal data is not optional—it is a prerequisite for survival. To receive a SASSA social grant, register for municipal electricity, or visit a public clinic, individuals must provide personal information. These transactions are non-negotiable; refusing to share data means losing access to essential services.

    The 2017 Cash Paymaster Services scandal is a stark example: biometric data of 17 million grant recipients was held by a private company without adequate safeguards, leading to widespread concerns about identity theft and surveillance. While POPIA now imposes stricter rules, the power imbalance remains—vulnerable individuals cannot simply walk away from these services.

    Gender-Based Violence: When Data Leaks Are Lethal

    South Africa has one of the highest rates of gender-based violence globally. For survivors, a data breach can be life-threatening. Leaked addresses, phone numbers, or workplace details can enable stalkers and abusers to locate their victims. Protection orders and domestic violence shelters rely on confidential data handling, yet POPIA’s enforcement mechanisms are rarely used in GBV cases.

    The National Register for Sex Offenders has faced criticism for weak access controls, and digital stalking via leaked personal data is a growing concern. While POPIA provides a legal basis for action, survivors often lack the resources to pursue complaints, and the Information Regulator has limited capacity to investigate every case.

    The Informal Economy: Outside the Law’s Reach

    An estimated 2.5 to 3 million South Africans work in the informal sector—spaza shop owners, hawkers, domestic workers, and gig economy participants. These workers often have no formal contracts, meaning their personal data is held by informal networks, community leaders, or micro-lenders with no compliance obligations.

    Micro-lenders, commonly known as “mashonisas,” frequently collect personal information—including copies of IDs and bank statements—without any privacy safeguards. If this data is misused, victims have little recourse, as POPIA’s jurisdiction over informal actors is unclear and enforcement is practically impossible.

    Children and the Elderly: Hidden Vulnerabilities

    Children in state care and child-headed households are particularly exposed. Their data may be held by multiple government agencies, with limited oversight. Similarly, elderly persons in rural areas often rely on caregivers or family members to manage their affairs, leaving them vulnerable to identity theft or financial exploitation.

    POPIA includes provisions for children’s privacy, but implementation is lagging. The Information Regulator has published guidance notes, but there is little evidence of proactive enforcement in these areas.

    Bridging the Gap: What Needs to Change

    To ensure POPIA benefits all South Africans, several steps are needed:

    • Community-based education: Privacy awareness campaigns should be conducted in local languages, using accessible formats like radio and community workshops.
    • Strengthened enforcement: The Information Regulator needs more resources and a mandate to investigate informal sector data practices.
    • Data protection by design: Government services like SASSA must embed privacy safeguards into their systems, not as an afterthought.
    • Legal aid for vulnerable groups: Survivors of GBV, migrants, and informal workers need accessible channels to lodge complaints and seek redress.
    • Regulation of informal data brokers: Micro-lenders and other informal actors should be brought under POPIA’s umbrella, with simplified compliance requirements.

    Conclusion

    South Africa’s privacy law is a significant achievement, but it is only as strong as its implementation. For the most vulnerable, privacy is not a luxury—it is a matter of safety, dignity, and survival. Without targeted efforts to bridge the digital divide, enforce the law in informal sectors, and protect those who cannot protect themselves, POPIA risks becoming another well-intentioned law that leaves the poorest behind. The Information Regulator, government, and civil society must act now to ensure that privacy is a right for all, not just the privileged few.

    Summary

    • POPIA is a strong law, but its benefits are unevenly distributed; vulnerable populations lack digital literacy and bargaining power.
    • The digital divide means many low-income South Africans access the internet via shared devices, compromising privacy.
    • Essential services like SASSA grants require data sharing, leaving vulnerable individuals with no choice but to comply.
    • GBV survivors face life-threatening risks from data leaks, yet enforcement is weak.
    • Informal sector workers and micro-lenders operate outside POPIA’s reach, leaving data unprotected.

    FAQ

    Q: What is POPIA?
    A: POPIA is South Africa’s Protection of Personal Information Act, which came into full effect on 1 July 2021. It sets rules for how personal data must be handled, including conditions for lawful processing and penalties for non-compliance.

    Q: Why are vulnerable people more at risk under POPIA?
    A: Vulnerable groups often lack digital literacy, rely on shared devices, and have no choice but to share data for essential services. They are also less likely to know their rights or be able to enforce them.

    Q: How does POPIA protect survivors of gender-based violence?
    A: POPIA requires strict handling of sensitive data, including addresses and health information. However, enforcement is weak, and survivors may not have the resources to lodge complaints, leaving them exposed to data leaks that could endanger their lives.

    Q: Does POPIA apply to informal sector workers and micro-lenders?
    A: In theory, yes, but in practice, informal actors often operate outside the law. The Information Regulator has limited capacity to investigate, and many informal workers are unaware of their rights.

    Q: What can be done to improve privacy protection for vulnerable South Africans?
    A: Community education, stronger enforcement, data protection by design in government services, legal aid for vulnerable groups, and regulation of informal data brokers are key steps.

  • BMW’s New Dashboard Ads: A ‘Treat’ or a Slippery Slope?

    BMW’s New Dashboard Ads: A ‘Treat’ or a Slippery Slope?

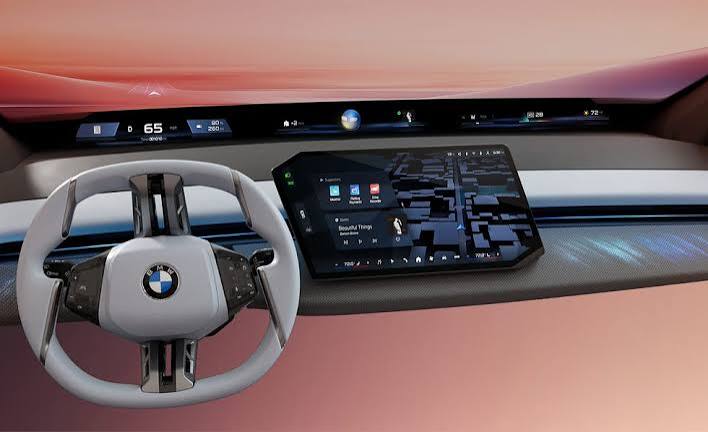
    Imagine sitting in your parked BMW, ready to head out, when a notification pops up on the dashboard screen: ‘Enjoy your drive? Consider upgrading to our premium navigation package!’ It’s not a glitch—it’s an advertisement, delivered directly to your car’s infotainment system. BMW is now showing ads on the dashboard screens of its vehicles, and the company is framing this as a ‘treat’ for drivers, a value-add to the connected car experience. But is this a harmless perk or a troubling shift in the relationship between automakers and car owners?

    The New Reality: Ads in Your Car

    BMW has begun pushing advertisements to the central infotainment displays of its vehicles. These ads appear via over-the-air (OTA) updates, which means they can be delivered remotely without a trip to the dealership. The content so far has been limited to BMW’s own services—like promoting digital features, maintenance packages, or accessories. For example, you might see a prompt to book a service appointment or to subscribe to a premium feature. The ads are designed to appear during idle moments, such as when the car is parked or at startup, minimizing distraction while driving.

    Why BMW Is Doing This

    Automakers are facing shrinking profit margins on vehicle sales. The industry is pivoting to recurring revenue streams: subscriptions, connected services, and data monetization. BMW has been a pioneer in this space, with controversial moves like charging a subscription for Apple CarPlay (later reversed) and offering heated seats as a paid feature. In-car advertising is a natural extension of this strategy. By showing ads, BMW can generate additional income, potentially subsidizing the cost of connected services or boosting their bottom line.

    The Industry Trend: You’re Not Alone

    BMW is not the first to explore this territory. Ford patented technology for displaying ads on in-car screens in 2023. General Motors announced plans for in-car advertising in 2022, but walked back after public backlash. Tesla has experimented with ads and premium connectivity tiers, though it has avoided intrusive ads on the main display. Stellantis (the parent of Jeep and Ram) has discussed ‘data monetization’ and in-car ad opportunities. The infrastructure is already in place: modern cars run on sophisticated infotainment systems with internet connectivity, making it technically trivial to push ads.

    The Consumer Backlash: Why People Are Upset

    For many drivers, the idea of ads in a car they paid $50,000 or more for feels like a violation. It’s a fundamental shift in the ownership experience. When you buy a car, you expect to own the hardware and control what appears on its screens. Ads challenge that expectation. There are also safety concerns. Even if ads appear only when parked, the potential for distraction during navigation or at stoplights is worrying. Critics also see this as a slippery slope: if BMW starts with its own services, third-party ads for coffee shops or gas stations are likely next. And ads require data—about your location, driving habits, and preferences—raising privacy concerns.

    The Pro-BMW Argument: A Value Exchange

    BMW might argue that ads are a fair trade: they subsidize the cost of connected services, allowing features like real-time traffic or remote services to be offered at lower prices. If the ads are relevant and helpful—like reminding you to book a service appointment—they could be seen as useful notifications rather than intrusive marketing. Drivers can dismiss them, and they appear only in non-driving moments. In a world where streaming services and mobile apps have normalized ad-supported tiers, cars may be the next frontier.

    The Regulatory Gray Area

    Currently, there is little to no regulation specifically governing in-car advertising. Privacy laws like GDPR in Europe and CCPA in California may apply to data collection used for ad targeting, but the display of ads itself is largely unregulated. Consumer protection laws could be invoked if ads are misleading or if BMW frames them as ‘features’ without clear disclosure. However, the legal landscape is still catching up to this new reality.

    What This Means for You

    If you own a BMW, you might start seeing these ads soon. You can ignore them, but they’re likely here to stay. The bigger question is whether this trend will spread to other automakers. Given the industry’s financial pressures, it’s plausible that in-car ads become as common as ads on streaming platforms. As a consumer, it’s important to be aware of this shift and to voice your opinions—automakers have reversed course before in the face of public backlash, as GM did in 2022.

    BMW’s dashboard ads are a test balloon for the automotive industry. While the company frames them as a ‘treat,’ many drivers see them as an intrusion. The outcome will depend on consumer reaction and regulatory response. For now, the next time you see an ad on your car’s screen, remember: it’s not just a notification—it’s a sign of where the industry is heading.

    Summary

    • BMW is showing ads on dashboard screens, delivered via over-the-air updates, initially for its own services.
    • Automakers are exploring in-car ads as a new revenue stream due to shrinking margins on vehicle sales.
    • Consumers are concerned about ownership rights, safety, privacy, and the potential for third-party ads.
    • Regulations are currently sparse, but privacy laws may apply to data collection for ad targeting.
    • The trend is industry-wide, with Ford, GM, Tesla, and Stellantis all exploring similar ideas.

    FAQ

    Q: Will I see ads while driving?
    A: BMW says ads appear only during idle moments, like when parked or at startup, to minimize distraction. However, the potential for ads during navigation or at stoplights remains a concern.

    Q: Can I opt out of seeing these ads?
    A: Currently, there’s no clear opt-out mechanism. BMW frames the ads as a value-add, so they may be part of the connected services experience. You can dismiss them, but they may reappear.

    Q: Are these ads for third-party products?
    A: So far, ads are for BMW’s own services and products. But the infrastructure could support third-party ads in the future, which is a major concern for critics.

    Q: How does BMW deliver these ads?
    A: Through over-the-air (OTA) updates, which allow BMW to push content to the car’s infotainment system remotely, without a dealer visit.

    Q: Is this legal?
    A: There’s little regulation specifically on in-car ads. Privacy laws like GDPR and CCPA may apply to data collection, but the display of ads is largely unregulated for now.

  • Canada Quietly Signs UN Cybercrime Treaty: A Surveillance Pact in Disguise?

    Canada Quietly Signs UN Cybercrime Treaty: A Surveillance Pact in Disguise?

    In late 2025, Canada quietly signed the United Nations Convention on Cybercrime, a treaty that aims to harmonize cybercrime laws globally. But critics warn that beneath its crime-fighting surface, the treaty contains provisions that could enable mass surveillance and undermine civil liberties. The signing, which occurred with little public debate or parliamentary scrutiny, has raised alarms among privacy advocates who see it as a backdoor to expanded state powers.

    This article unpacks what the treaty actually says, why Canada signed it, and what it could mean for your digital rights. We’ll explore the fine print on data collection, the vague ‘prevention’ clause, and the geopolitical chess game that led to this moment. By the end, you’ll understand why this seemingly technical treaty is anything but mundane.

    What Is the UN Cybercrime Convention?

    Formally known as the ‘United Nations Convention on Countering the Use of Information and Communications Technologies for Criminal Purposes,’ this treaty was adopted by the UN General Assembly in December 2024. It’s a broad agreement that requires signatories to criminalize a range of cyber offenses—from illegal access to data interference, fraud, and child sexual abuse material. It also sets up frameworks for international cooperation, including mutual legal assistance and extradition.

    But the treaty goes beyond simple crime-fighting. It includes provisions for real-time collection of traffic data and preservation of electronic evidence. These are tools that law enforcement agencies love, but they come with significant privacy implications. The treaty also has a controversial ‘prevention’ clause that critics argue could be used to justify broad surveillance or content moderation mandates.

    The Quiet Signing: Why No One Noticed

    Canada signed this treaty in 2025–2026 with almost no public fanfare. There were no major press conferences, no parliamentary debates, and no consultations with civil society. This is a stark contrast to how Canada typically handles major international agreements. The government’s silence has led to accusations that it’s trying to sneak a surveillance-friendly treaty past the public.

    Why the secrecy? One possibility is that the government knows the treaty is controversial. Another is that it’s part of a broader strategy to engage with the UN process to counter Russian and Chinese influence. But whatever the reason, the lack of transparency is troubling for a treaty that could affect the digital rights of every Canadian.

    The Surveillance Provisions: What’s in the Fine Print?

    Let’s break down the most concerning parts of the treaty. First, there’s the real-time collection of traffic data. This means that internet service providers (ISPs) could be required to hand over information about who you’re communicating with, when, and from where—in real time. This is different from wiretapping, which captures the content of communications. Traffic data is metadata, and it can reveal a lot about your life, even if the content of your messages remains private.

    Second, the treaty requires signatories to preserve electronic evidence. This sounds benign, but it can mean that companies must store data for long periods, even if there’s no ongoing investigation. This could lead to data retention mandates that force companies to keep logs of your online activities for months or years.

    Third, the ‘prevention’ clause is vague. It says that countries should take measures to prevent cybercrime, but it doesn’t define what those measures are. This could be interpreted to require ISPs and platforms to monitor content for illegal activity, which would be a form of mass surveillance. It could also be used to pressure companies to weaken encryption, which would make everyone less secure.

    The Budapest Convention: A Better Alternative?

    Canada is already a party to the Budapest Convention on Cybercrime, which has been the gold standard for international cybercrime cooperation since 2001. The Budapest Convention has strong human rights protections and requires that any data collection be subject to due process. The UN treaty, in contrast, has weaker safeguards, which is why many experts see it as a step backward.

    Why would Canada sign a weaker treaty when it already has a better one? The answer may lie in geopolitics. The UN treaty was a Russian-led initiative, and by signing it, Canada can have a seat at the table when the rules are being written. But critics argue that this legitimizes a treaty that could be used by authoritarian states to justify surveillance of dissidents and journalists.

    What Does This Mean for Canadians?

    If Canada ratifies the treaty, it will need to update its laws to comply. This could mean changes to the Criminal Code and the Privacy Act. The government might argue that existing laws already meet the treaty’s requirements, but the treaty’s vague language could be used to push for more expansive surveillance powers.

    For ordinary Canadians, the most immediate impact could be on your online privacy. If ISPs are required to collect and store traffic data, that information could be accessed by law enforcement without a warrant in some cases. The treaty also creates a framework for sharing evidence across borders, which could make it easier for foreign governments to request data about Canadians.

    The Geopolitical Angle: Why Canada Signed

    Canada’s decision to sign is not just about cybercrime; it’s about international relations. The UN treaty was adopted with support from many Global South countries, who see it as a way to get technical assistance and capacity building. By signing, Canada can help shape how the treaty is implemented, potentially pushing for stronger human rights protections.

    But there’s a risk: by signing, Canada lends legitimacy to a treaty that could be used to justify authoritarian surveillance. Some argue that boycotting the treaty would be worse, as it would leave the field open to Russia and China to define the norms. It’s a delicate balance, and the Canadian government seems to be betting that it can influence the treaty from within.

    The Path to Ratification: Still a Chance for Debate

    Signing is just the first step. The treaty will only enter into force after 40 countries ratify it, and as of early 2026, fewer than 20 have done so. In Canada, ratification requires parliamentary approval, which means there’s still time for public debate. Civil society groups are already calling for hearings and consultations, and it’s possible that the government will face pressure to add reservations or interpretative declarations to protect Canadians’ rights.

    If you’re concerned about this treaty, now is the time to speak up. Contact your MP, join privacy advocacy groups, and demand that the government be transparent about its intentions. The treaty may have been signed quietly, but its impact could be loud and lasting.

    Canada’s quiet signing of the UN Cybercrime Convention is a wake-up call for anyone who cares about digital rights. The treaty’s surveillance-friendly provisions, combined with the lack of public debate, make it a dangerous precedent. While signing doesn’t mean immediate ratification, it sets the stage for a potential erosion of privacy protections. Canadians must demand transparency and accountability before this treaty moves any further.

    Summary

    • Canada signed the UN Cybercrime Convention in 2025–2026 with little public or parliamentary scrutiny.
    • The treaty includes provisions for real-time traffic data collection and electronic evidence preservation, which could enable mass surveillance.
    • The vague ‘prevention’ clause could be used to justify content monitoring or weakened encryption.
    • Canada is already a party to the stronger Budapest Convention, raising questions about why it signed a weaker treaty.
    • The treaty is not yet ratified; there is still time for public debate and parliamentary oversight.

    FAQ

    Q: What is the UN Cybercrime Convention?
    A: It’s a UN treaty adopted in December 2024 that requires countries to criminalize cybercrimes and cooperate internationally. It includes provisions for data collection and evidence sharing that worry privacy advocates.

    Q: Why is Canada’s signing controversial?
    A: Because it happened quietly, without public debate, and the treaty’s provisions could be used to justify surveillance and data retention that infringe on privacy rights.

    Q: How does this treaty differ from the Budapest Convention?
    A: The Budapest Convention has stronger human rights protections and due process requirements. The UN treaty is seen as weaker, with vaguer language that could be exploited by authoritarian governments.

    Q: What can I do to stop it?
    A: Contact your Member of Parliament, support privacy advocacy groups, and demand that the government hold public consultations before ratification.

    Q: Will this affect my online privacy?
    A: If ratified, it could lead to laws requiring ISPs to collect and store traffic data, which law enforcement could access. This could make it easier for authorities to track your online activities.