Tag: cybersecurity

  • How OpenAI Caught a Russian AI Influence Campaign (And What It Means for You)

    How OpenAI Caught a Russian AI Influence Campaign (And What It Means for You)

    In a recent blog post, OpenAI announced that it had disrupted a covert influence operation originating from Russia. The campaign used ChatGPT to generate fake social media profiles, write posts, and amplify divisive narratives. This is not the first takedown of its kind, but it highlights a growing challenge: as AI tools become more powerful and accessible, they also become attractive weapons for state-sponsored disinformation.

    OpenAI says it identified the network, terminated the associated accounts, and shared threat intelligence with industry partners. But what does this mean for the average internet user? And how effective are these takedowns in the long run? Let’s break down the details, the limitations, and the broader implications.

    The Anatomy of the Campaign

    OpenAI’s report describes a network of accounts that used ChatGPT to generate content for fake social media profiles. The operation was attributed to Russian actors, though the company did not name a specific group with absolute certainty. The content was designed to amplify divisive narratives likely on topics such as politics, social issues, or international conflicts with the goal of sowing discord.

    What’s notable is the scale that AI enables. Traditional troll farms, like the Internet Research Agency, required hundreds of human operators to write posts and manage accounts. With generative AI, a small team can produce thousands of pieces of content in multiple languages, each tailored to specific audiences. This lowers the cost of influence operations and makes them harder to detect, as the language can be varied to avoid pattern recognition.

    OpenAI did not disclose the exact number of accounts or posts removed, but stated that the operation was “disrupted”—meaning the accounts were deactivated and the content was removed from platforms. The company also emphasized that it shares threat intelligence with partners like social media companies and other AI labs.

    How Attribution Works (and Why It’s Not Always Certain)

    When OpenAI attributes an operation to Russia, it relies on a combination of technical indicators and behavioral patterns. These might include the IP addresses used to create accounts, the language and style of the generated content, and the infrastructure that hosted the operation. However, these indicators can be spoofed. A third party could deliberately use Russian-language content and Russian servers to frame the country. Therefore, attribution is probabilistic, not absolute.

    OpenAI’s report likely used language like “with moderate confidence” to acknowledge this uncertainty. This is standard practice in cybersecurity, where false flags are a known tactic. For example, in 2020, a group linked to Iran was caught posing as Russian actors online. So while the evidence points to Russian involvement, it’s worth remembering that nothing is 100% certain in cyberspace.

    The Limits of Takedowns

    Even when OpenAI successfully identifies and removes accounts, the impact may be limited. The same actors could simply set up new accounts using a different AI service or open-source models like Llama. They might also move to platforms that are less cooperative or use encrypted messaging apps that are harder to monitor.

    Moreover, publicizing takedowns has a dual effect. On one hand, it helps defenders by raising awareness and sharing threat intelligence. On the other hand, it teaches adversaries how to evade detection next time. They learn what patterns were caught and can adjust their behavior accordingly.

    OpenAI only controls its own ecosystem. It can block accounts that use ChatGPT, but it cannot prevent the content from being re-posted elsewhere. Once text is generated, it can be copied to any platform, making it nearly impossible to retract.

    The Broader Context: AI and Influence Operations

    This takedown is part of a larger trend. Since at least 2023, AI-generated content has been used in influence operations by various countries, including Iran, China, and Russia. In the run-up to the 2024 elections, there was a record amount of AI-generated political content globally, much of it designed to mislead or polarize.

    AI’s advantage for bad actors is not just speed, but also adaptability. An LLM can be instructed to write in a particular style, target specific demographics, or even mimic the tone of a particular political group. This makes the content more convincing and harder to spot.

    However, it’s important to note that AI did not act autonomously. Human operators directed the campaign, choosing the narratives and deciding where to post. The AI was simply a tool, albeit a powerful one.

    What Can You Do to Stay Informed?

    For the average person, the existence of such campaigns is unsettling, but there are steps you can take to reduce your susceptibility to disinformation:

    • Check the source: If a post seems inflammatory, look up the account that posted it. Is it recently created? Does it have a history of posting similar content? Fake profiles often lack organic engagement.
    • Look for patterns: AI-generated content may have subtle tells, such as generic phrasing or an unnatural consistency in tone. However, these are becoming less reliable as models improve.
    • Cross-verify: Before sharing something, see if reputable news outlets are reporting the same facts. If it’s only on social media, it might be false.
    • Be skeptical of emotional appeals: Disinformation often plays on strong emotions like anger or fear. Take a moment to step back and consider whether the post is trying to manipulate you.

    OpenAI’s disruption of the Russian influence campaign is a positive step, but it’s not a silver bullet. As AI tools become more accessible, we can expect more such operations, not fewer. The responsibility falls on tech companies, governments, and individuals to work together to mitigate the risks. By understanding how these campaigns work and staying vigilant, we can better protect ourselves from manipulation.

    Summary

    • OpenAI disrupted a covert Russian influence operation that used ChatGPT to generate fake profiles and content.
    • The campaign aimed to amplify divisive narratives, but attribution is not 100% certain.
    • Takedowns are only partially effective; adversaries can adapt and move to other platforms.
    • AI-enabled influence operations are a growing trend, not a new phenomenon.
    • Individuals can reduce risk by checking sources, cross-verifying facts, and being skeptical of emotional posts.

    FAQ

    Q: Did AI create the campaign on its own?
    A: No. Human operators directed the campaign, using AI as a tool to generate content at scale. The AI did not act autonomously.

    Q: Is this the first time OpenAI has disrupted such a campaign?
    A: No. OpenAI has previously taken down operations linked to Iran, China, and Russia. This is part of an ongoing effort.

    Q: How does OpenAI attribute the campaign to Russia?
    A: Through technical indicators like IP addresses and behavioral patterns. However, attribution is probabilistic and could be a false flag.

    Q: Will this stop the disinformation?
    A: Not entirely. The same actors may use other platforms or open-source AI models. Takedowns are a temporary measure.

    Q: How can I spot AI-generated disinformation?
    A: Look for accounts that are new or lack organic engagement, and be wary of content that provokes strong emotions. Cross-verify facts with trusted sources.
  • Deepfake Job Scams: 3 New Tricks Draining Bank Accounts and How to Spot Them

    Deepfake Job Scams: 3 New Tricks Draining Bank Accounts and How to Spot Them

    Imagine acing a video interview, shaking hands (virtually) with a CEO, and getting hired on the spot. Then, you’re asked to pay for your own laptop or ‘training fee’ and the job vanishes, along with your money. This isn’t a plot twist; it’s a new wave of job scams powered by deepfakes.

    Cybercriminals are using AI-generated audio and video to impersonate recruiters and executives, creating hyper-realistic cons that have already drained bank accounts. The FBI’s Internet Crime Complaint Center reported investment fraud losses over $4.5 billion in 2023, with deepfake lures playing a significant role. Here are the three new scams you need to know about, and how to protect yourself.

    The Deepfake Threat Goes to Work

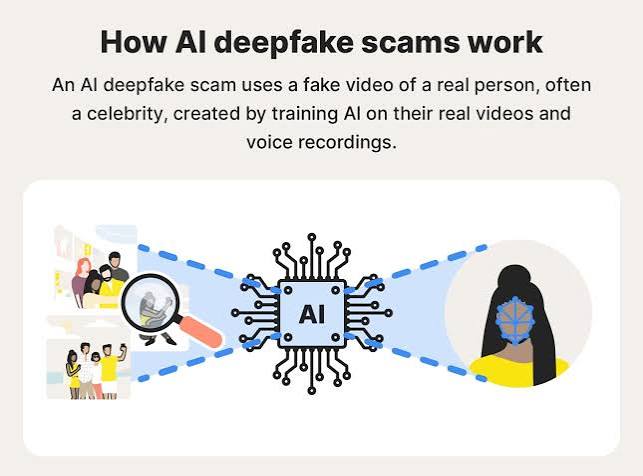
    Remote work has made hiring digital-first. Video interviews are standard, and onboarding often happens without a single in-person meeting. Scammers have exploited this shift, using AI tools to clone voices and faces with frightening accuracy. They scrape a few minutes of a real recruiter’s video from LinkedIn or a company’s YouTube channel, then use off-the-shelf software to create a fake version that can interview you live.

    What was once Hollywood-level VFX is now accessible to anyone with a laptop and a grudge against your bank account. The result? A surge in sophisticated job scams that are harder to spot than the old “Nigerian prince” emails.

    Scam 1: The Fake Interview Trap

    Picture this: You apply for a remote position at a well-known tech company. Within days, you get a Zoom invite from the “hiring manager.” The video call goes smoothly—the person looks and sounds exactly like the executive you researched. They offer you the job on the spot, but there’s a catch: you need to pay a “processing fee” for your work visa or “equipment deposit” for a company laptop.

    The deepfake makes it feel legitimate. You’ve seen this person on the company’s website. But once you wire the money, the “recruiter” vanishes, and the real company has never heard of you.

    How it works: Scammers create a deepfake of a real employee, often using publicly available footage. They conduct a live interview, sometimes even answering questions with pre-scripted responses. The urgency of the offer and the request for payment are designed to bypass your skepticism.

    Red flags: Legitimate employers never ask for money upfront. If a job offer requires any payment for equipment, training, or visas, it’s a scam. Also, be wary of interviews where the connection is poor or the person seems slightly off—glitches in lip-sync or unnatural blinking can be giveaways.

    Scam 2: The Crypto “Work-From-Home” Hustle

    This scam targets job seekers with promises of easy money in cryptocurrency trading. You’re hired as a “crypto asset manager” for a startup that seems legit—they have a polished website, glowing employee testimonials, and even video messages from the “founder.” Your job is to deposit your own money into a trading platform to “test” it or to “match” a company contribution.

    At first, the platform shows impressive returns. You invest more, encouraged by fake success stories featuring deepfake videos of supposed employees who claim they’ve made thousands. But when you try to withdraw, the platform freezes your account, and the company disappears.

    How it works: The deepfakes here are used to create convincing testimonials and “live” webinars. The entire company is a facade, built with AI-generated content to lure victims into depositing real money into a fake exchange.

    Red flags: Be skeptical of jobs that require you to invest your own money. Legitimate jobs pay you; they don’t ask you to pay them. Also, research the company independently—check if they’re registered with financial regulators and look for reviews on trusted sites.

    Scam 3: The Deepfake CEO Onboarding

    You’ve landed a remote job, completed your paperwork, and are ready to start. Then, you get a video call from the “CEO” or “CFO”—someone you recognize from the company’s website. They explain that there’s an urgent, confidential acquisition, and they need you to process a wire transfer to a vendor. Or they ask for your banking credentials for “payroll setup.”

    The deepfake is so convincing that you don’t think twice. You authorize the payment or share your login details, and your bank account is cleaned out.

    How it works: This scam exploits the trust you’ve already built with the fake employer. Scammers have access to your personal information from the initial application, making the request seem plausible. They use voice cloning and video deepfakes to impersonate high-level executives, creating a sense of urgency that pressures you into acting without verification.

    Red flags: No legitimate company will ask you to make urgent payments or share banking credentials over a video call. Always verify such requests through a separate communication channel, like a known phone number or official email. If it’s a real CEO, they’ll be reachable, and you can confirm.

    Why These Scams Are So Effective

    The deepfake element adds a layer of false legitimacy that classic scams lacked. When you see a familiar face, your brain goes into trust mode. The emotional high of getting a job offer, combined with the authority of a CEO, creates a powerful psychological hook.

    Moreover, the current job market is brutal. With mass layoffs in tech, many skilled professionals are desperate, and that desperation clouds judgment. Scammers exploit this by targeting recent graduates and those in financial distress, who are more likely to ignore red flags.

    How to Protect Yourself

    First, remember the golden rule: No legitimate employer will ever ask you for money. If you encounter any request for payment, it’s a scam.

    Second, verify independently. If you’re interviewing, contact the company directly through their official website or phone number to confirm the interviewer’s identity. Don’t use contact details provided in the suspicious email.

    Third, be wary of urgency. Scammers create false deadlines to rush you. Take a step back and think.

    Fourth, learn to spot deepfakes. Look for subtle anomalies: unnatural eye movement, slight audio lag, or a face that doesn’t quite match the lighting. But remember, deepfakes are getting better, so don’t rely solely on visual cues.

    Finally, if you suspect a scam, report it to the FBI’s IC3 and the Federal Trade Commission. Reporting helps law enforcement track these criminals and warn others.

    The Bigger Picture: An Arms Race

    Cybersecurity experts describe a constant battle between deepfake creators and detection tools. As detection improves, so do the fakes. The deeper issue is social engineering—the deepfake is just the hook; the real trick is manipulating human psychology.

    Legitimate companies are also victims. Recruiters find their faces and voices stolen, and their job postings are scraped and reposted with altered contact details. This erosion of trust affects everyone, making remote hiring more challenging.

    Regulation is lagging. Many countries lack specific laws against deepfake fraud, and the cross-border, crypto-based nature of these crimes complicates prosecution. Until laws catch up, awareness is your best defense.

    Deepfake job scams are a new twist on an old problem. By understanding the three main types—fake interviews, crypto schemes, and CEO impersonation—you can spot the red flags and protect your bank account. Always remember: if it feels too good to be true, it probably is. Stay vigilant, verify everything, and trust your instincts.

    Summary

    • Deepfake job scams use AI-generated audio/video to impersonate recruiters and executives, tricking victims into sending money.
    • Three dominant scams: fake interviews requesting fees, crypto work-from-home schemes requiring deposits, and CEO impersonation for urgent payments or banking details.
    • Losses can range from thousands to over $100,000, with investment fraud totaling $4.5 billion in 2023.
    • Target remote job seekers, especially in a tough job market, exploiting the lack of in-person verification.
    • Protect yourself: never pay for a job, verify independently, and report suspicious activity to the FBI’s IC3.

    FAQ

    Q: How do scammers create deepfakes of real people?
    A: They scrape publicly available videos and audio from social media, like LinkedIn or YouTube, then use AI tools to create a realistic clone that can speak and move like the real person.

    Q: Can I spot a deepfake during a video call?
    A: Look for subtle clues like unnatural blinking, slight lip-sync issues, or audio that’s out of sync. However, deepfakes are improving, so never rely solely on visual detection.

    Q: What should I do if I think I’ve been targeted?
    A: Stop all contact, don’t send any more money or information, and report the incident to the FBI’s IC3 (ic3.gov) and the Federal Trade Commission. Also, contact your bank to freeze accounts if you’ve shared credentials.

    Q: Are legitimate companies asking for fees during onboarding?
    A: No. Genuine employers cover costs like equipment and visas. Any request for payment from a job candidate is a major red flag.

    Q: How can I verify a job offer is real?
    A: Always contact the company directly using official channels from their website, not the contact info in the offer. Ask to speak with someone in HR and confirm your offer in writing.

  • Why Municipal Water Systems Are Sitting Ducks for Hackers

    Why Municipal Water Systems Are Sitting Ducks for Hackers

    In February 2021, an attacker at the Oldsmar, Florida water treatment plant remotely accessed the system’s HMI via TeamViewer and briefly boosted sodium hydroxide levels from 100 parts per million to 11,100 ppm a jump that could have turned the water supply into a caustic hazard. A plant operator spotted the cursor moving on screen and reversed the change before anyone was harmed. The attack was trivial: a shared password, an internet-exposed remote access tool, and no multi-factor authentication.

    Oldsmar wasn’t a one-off. Across the U.S., municipal water utilities rely on industrial control systems (ICS) and SCADA networks that were designed decades ago for reliability, not security. Many of these systems run on legacy firmware, communicate over protocols with no authentication, and are increasingly connected to the internet for convenience. The result: a critical infrastructure sector that is uniquely vulnerable to cyberattacks, with consequences that could threaten public health.

    The Anatomy of a Water Utility’s Control System

    To understand the vulnerabilities, you need to know the hardware. Municipal water systems use Supervisory Control and Data Acquisition (SCADA) systems to monitor and control everything from water treatment to distribution. The key components are Programmable Logic Controllers (PLCs) and Remote Terminal Units (RTUs)—small, specialized computers that open and close valves, start and stop pumps, and read sensors for pressure, flow, chlorine levels, and water levels.

    These devices are the workhorses of the water system. They run on firmware that often hasn’t been updated in years, and they communicate over protocols like Modbus and DNP3 that were designed in an era when no one imagined they’d be connected to the internet. These protocols have zero authentication and no encryption. Anyone who can reach the network can send commands as if they were the operator.

    In the past, that was okay because these systems were air-gapped—physically isolated from other networks. But that’s eroded. Utilities now connect their OT networks to IT networks for remote monitoring, billing, and compliance. The air gap has become a porous membrane, and attackers have found the holes.

    How Attackers Get In

    Attackers use a variety of vectors to breach water utilities, and many of them are embarrassingly simple.

    Internet-exposed devices. Shodan, a search engine for internet-connected devices, routinely shows HMIs and PLCs accessible to anyone. Many have default credentials like “admin/admin” or no password at all. In one 2023 incident reported by CISA, an attacker changed a pump’s operational parameters after finding the HMI exposed online.

    Phishing and lateral movement. A classic approach: phish an employee in the IT department, get a foothold in the corporate network, then pivot to the OT network. The 2015 Ukraine power grid attack used this technique, and water utilities share similar architectures.

    VPN and remote access vulnerabilities. Utilities often use VPNs for remote access, but these appliances may be unpatched. In 2021, a ransomware group hit a water treatment plant in California by exploiting a known vulnerability in a VPN appliance.

    Supply chain and third-party access. Vendors and contractors often have standing remote access to multiple utilities. If an attacker compromises a vendor, they can reach any utility that trusts that vendor’s credentials. This is a single point of failure that affects many small utilities.

    Physical access. USB drops, direct connection to serial ports, or engineering workstations left unsecured. It’s not glamorous, but it works.

    Water-specific protocol attacks. Attackers can inject false sensor readings—telling the system a tank is full when it’s empty—or send direct commands to valves and pumps. The Oldsmar attack was a direct command to increase lye dosage.

    Real-World Incidents: From Sewage to Lye

    The threat isn’t theoretical. Here are some notable cases:

    • Oldsmar, Florida (2021): As described, an attacker used TeamViewer to access the HMI and tried to poison the water supply. It was stopped by a sharp-eyed operator.
    • Maroochy Shire, Australia (2000): A disgruntled former contractor used radio equipment and stolen software to release 800,000 liters of raw sewage into waterways over three months. This is the classic insider attack.
    • Ukraine (2015/2016): Though primarily power grids, the BlackEnergy and Industroyer malware demonstrated how OT systems can be remotely manipulated. Water utilities run on similar architectures.
    • Israel (2020): State actors attempted attacks on water infrastructure, targeting chlorine dosing and other control systems.
    • Multiple U.S. incidents (2023–2024): CISA reported intrusions at water facilities via internet-exposed HMIs and default passwords, including one where an attacker changed a pump’s operational parameters.

    These incidents show a range of attackers—from disgruntled insiders to nation-states—and a common theme: the systems are vulnerable because they were never designed with security in mind.

    Why Water Utilities Are Uniquely Vulnerable

    There are about 150,000 public water systems in the U.S. alone. The vast majority serve small populations with tiny IT budgets and no dedicated security staff. A town of 2,000 people doesn’t have a CISO.

    Legacy infrastructure is another factor. Pumps and pipes can last 50 years, and the control systems are often just as old. It’s not uncommon to find Windows XP machines running a treatment plant’s SCADA system. These unsupported operating systems are riddled with known vulnerabilities that will never be patched.

    Safety vs. security trade-offs are baked into the design. Water systems are engineered for reliability and fail-safe operation. If a sensor fails, the system should default to a safe state. But that also means availability trumps confidentiality and integrity. Attackers can exploit this by forcing the system into unsafe states.

    The human factor is huge. Operators often share passwords, use default credentials, and leave remote access tools like TeamViewer and AnyDesk installed for vendor convenience. Vendors may have standing access to dozens of utilities, creating a single point of compromise. Turnover and lack of documentation mean accounts are rarely deactivated when employees leave.

    Cost constraints make it hard to fix these problems. Small utilities can’t afford modern SCADA upgrades, network segmentation, or 24/7 monitoring. The result is a sector that is underfunded, understaffed, and under attack.

    The Threat Landscape: Who’s Attacking and Why

    The attackers range from nation-state actors to cybercriminals. Nation-states target water infrastructure for espionage, disruption, or retaliation. Israel’s 2020 attacks were attributed to state actors. Cybercriminals have also hit water utilities with ransomware—in 2021, a ransomware attack on a California water facility forced operators to switch to manual control.

    These attacks can have real consequences. An attacker who manipulates chlorine levels could cause a public health crisis. One who opens a valve could flood a town. The potential for physical harm distinguishes water utilities from typical data breaches.

    The Regulatory Landscape: Gaps and Progress

    In the U.S., CISA and the EPA oversee water sector cybersecurity. The America’s Water Infrastructure Act (AWIA) requires utilities to conduct risk assessments and prepare emergency response plans, but it doesn’t mandate cybersecurity standards. Many incidents go unreported—utilities fear reputational damage or fines.

    CISA has issued emergency directives requiring action for known exploited vulnerabilities, and the Biden administration has proposed cybersecurity requirements for public water systems. The EPA has even taken enforcement actions against non-compliant utilities. But progress is slow, and the gap between large and small utilities remains wide.

    What Can Be Done

    The fixes are known but require investment and political will. Network segmentation can isolate OT networks from IT networks. Multi-factor authentication would have stopped Oldsmar. Regular patching of known vulnerabilities closes the most common attack paths. And training operators to recognize phishing attempts could prevent initial compromise.

    But for the thousands of small utilities, these solutions may seem out of reach. That’s where federal assistance and sector-wide initiatives come in. The threat is real, and the time to act is now—before an attack succeeds.

    Municipal water systems are critical infrastructure, yet they remain dangerously exposed. The technology is old, the budgets are thin, and the attackers are sophisticated. But the fixes are known: segment networks, require multi-factor authentication, patch vulnerabilities, and train staff. The next Oldsmar might not have a quick-thinking operator to stop it.

    Summary

    • Municipal water systems rely on legacy SCADA and ICS systems that lack modern security features.
    • Attack vectors include internet-exposed devices, phishing, VPN exploits, and third-party access.
    • Real-world incidents like Oldsmar, Florida and Maroochy Shire show the potential for physical harm.
    • Fragmented ownership, legacy infrastructure, and cost constraints make utilities uniquely vulnerable.
    • Regulatory gaps persist, but CISA and EPA are taking steps to enforce better security.

    FAQ

    Q: What is SCADA and why is it used in water systems?
    A: SCADA (Supervisory Control and Data Acquisition) systems monitor and control water treatment, storage, and distribution. They use PLCs and RTUs to automate valves, pumps, and sensors.

    Q: How did the Oldsmar attack happen?
    A: The attacker accessed the plant’s HMI via TeamViewer using a shared password and increased sodium hydroxide levels. An operator spotted it and reversed it.

    Q: Why are water utilities so vulnerable?
    A: They have legacy equipment, lack cybersecurity budgets, and often rely on default credentials and unpatched systems. The OT networks are increasingly connected to IT networks, creating attack paths.

    Q: What can a hacker do to a water system?
    A: They can change chemical dosing, manipulate valve positions, or disrupt pumps, potentially causing contamination, flooding, or service outages.

    Q: Is there regulation for water system cybersecurity?
    A: The America’s Water Infrastructure Act requires risk assessments, but mandatory cybersecurity standards are still being developed. CISA and EPA are increasing oversight.

  • GTA 6 JUST LEAKED… And It’s WAY Bigger Than We Thought

    GTA 6 JUST LEAKED… And It’s WAY Bigger Than We Thought

    Bloomberg has dropped a new report on what is happening inside Rockstar Games following the GTA 6 leaks: - Rockstar employees are feeling “frustrated and exhausted” - An exec at Rockstar has

    In September 2022, Rockstar Games experienced a breach that flooded the internet with over 90 videos and screenshots of an early development build of Grand Theft Auto VI. The leak showcased a male and female protagonist (later identified as Jason and Lucia), a return to Vice City, and rough gameplay mechanics all before Rockstar was ready to reveal anything officially. For a studio known for its ironclad secrecy, this was an unprecedented violation. But beyond the initial shock, the leak raised serious questions about security, fan expectations, and the true cost of a stolen glimpse at a highly anticipated game.

    The Leak and Its Fallout

    The leaked footage surfaced on a gaming forum, showing unpolished animations, placeholder assets, and debug menus clearly years away from the final product. Rockstar responded with a public statement acknowledging the “network intrusion” and expressing disappointment. They reassured fans that development would continue and the final game would be “exactly as we intend.” But the damage was done: millions of views, countless news articles, and a permanent mark on the game’s pre-release history.

    Who Was Behind the Hack?

    Authorities later identified Arion Kurtaj, an 18-year-old from Oxford, UK, as the hacker. He was part of the Lapsus$ group, a cybercrime gang known for targeting tech giants like Microsoft, Samsung, and Nvidia using social engineering and SIM-swapping—methods that are low-tech but devastatingly effective. Kurtaj was convicted in 2023 and sentenced to an indefinite hospital order, a reflection of his vulnerability and the seriousness of the crime.

    Rockstar’s Perspective: A Managed Vision, Compromised

    Rockstar’s secrecy isn’t just a preference; it’s a strategy. The company carefully orchestrates every reveal, from teaser trailers to gameplay showcases, to maximize impact. This leak bypassed that control entirely, exposing raw, unfinished work that the developers never intended for public consumption. Take-Two Interactive, Rockstar’s parent company, has aggressively pursued legal action against those who distributed the content, estimating millions in damages—though the exact figure remains disputed.

    Fan Reactions: Excitement vs. Resignation

    Many fans were thrilled to see even a rough cut of the game. The leak confirmed long-standing rumors: the Vice City setting, the dual protagonists, and the ambitious scope. Some argued it generated more hype than any official trailer could. Others felt the surprise was ruined, and the poor quality of the footage gave a misleading impression. The debate highlighted a fundamental tension: fans crave information, but Rockstar wants to control the narrative.

    Debunking Common Misconceptions

    One of the most widespread misunderstandings is that the leaked footage represents the final look of GTA 6. It doesn’t. The builds were years old, with placeholder graphics and unoptimized code. Another myth: the leak was a publicity stunt. There’s no evidence for this; Rockstar has a history of fighting leaks and took legal action. Similarly, the leak didn’t cause a delay—the game was already expected to be years away. And the hacker wasn’t a whistleblower or hacktivist; he was a convicted criminal seeking notoriety.

    The Broader Industry Context

    GTA 6 isn’t an isolated case. The gaming industry has seen a wave of cyberattacks, from the 2020 Nintendo source code leak to the 2023 Insomniac Games breach. These incidents underscore a growing vulnerability: developers hold vast amounts of valuable data, and security often lags behind creativity. While Rockstar’s response was swift, the leak serves as a cautionary tale for the entire industry—and a reminder that even the most secretive studios aren’t immune.

    The GTA 6 leak was a seismic event in gaming culture, exposing the fragility of even the most guarded corporate secrets. For Rockstar, it was a costly and demoralizing breach. For fans, it was a premature glimpse into a world they’d have to wait years to fully explore. As the game finally inches toward an official reveal, the leaked footage remains a curious artifact—a reminder that in the digital age, nothing stays hidden forever.

    Summary

    • A 2022 breach leaked 90+ videos and screenshots of GTA 6’s early development build, including protagonists Jason and Lucia and the Vice City setting.
    • Rockstar confirmed the hack, called it a “network intrusion,” and vowed to continue development as intended.
    • The hacker, Arion Kurtaj, was convicted and sentenced to an indefinite hospital order in 2023.
    • The leak caused millions in damages, but no official delay has been announced.
    • The leaked footage is not representative of the final game, and the leak was a criminal act, not a publicity stunt.

    FAQ

    Q: Was the leaked GTA 6 footage real?
    A: Yes, the footage was genuine early development material, but it was years old and unpolished, showing placeholder assets and debug tools.

    Q: Did the GTA 6 leak delay the game’s release?
    A: No official delay has been attributed to the leak; the game was already expected to be years away from launch.

    Q: Who was responsible for the GTA 6 hack?
    A: Arion Kurtaj, an 18-year-old member of the Lapsus$ hacking group, was convicted for the breach.

    Q: Will the final GTA 6 look like the leaked footage?
    A: No, the final game will be significantly more polished and different from the early build shown in the leak.

    Q: Why is Rockstar so secretive about GTA 6?
    A: Rockstar carefully controls reveals to maximize impact and manage expectations, a strategy that the leak disrupted.

  • The GTA 6 Leak Nobody Saw Coming: Inside the Biggest Breach in Gaming History

    The GTA 6 Leak Nobody Saw Coming: Inside the Biggest Breach in Gaming History

    CONFIRMED: The GTA 6 leaks are from 2025. ✓ The leaked build is at least from 2025, as Tate McRae's “Sports Car,” heard in the footage, was released in January 2025.

    In September 2022, a hacker going by “teapotuberhacker” posted over 90 videos and screenshots of an unfinished Grand Theft Auto VI on a public forum. The footage showed a female protagonist, a neon-soaked Vice City, and glitchy animations straight from an internal dev build. It was the single largest leak in gaming history—and it happened not through sophisticated malware, but a teenager with a SIM-swap.

    Rockstar Games, known for its ironclad secrecy, confirmed the leak was real, calling it “extremely distressing” for the team. For fans who had waited over a decade since GTA V, it was a tantalizing glimpse. For developers, it was a nightmare. This is the story of how a 17-year-old from Oxford brought a billion-dollar company to its knees—and what it means for the future of game development.

    The Leak That Broke the Internet

    At 1:00 AM on September 18, 2022, a user on GTAForums posted a link to a folder of videos. The post read simply: “GTA VI – 90+ clips.” Within hours, the clips were everywhere—Telegram, YouTube, Twitter. The footage was raw: characters floating through walls, cars with placeholder physics, and a female protagonist named Lucia in a Miami-inspired Vice City. It was unmistakably GTA 6, and it was unfinished.

    The leak included not just gameplay but source code for GTA V and Red Dead Redemption 2, internal developer builds, and even Slack messages. Rockstar’s response was swift: a statement confirming the authenticity, a plea to fans not to share the material, and a wave of DMCA takedowns across social media. Take-Two Interactive’s stock dropped 6% in the following days.

    Who Was Behind It?

    The hacker claimed to be the same person behind a recent Uber breach. Investigators soon identified him as Arion Kurtaj, a 17-year-old from Oxford, England, and a member of the Lapsus$ hacking group. Lapsus$ was a loosely organized collective known for social engineering and SIM-swapping—not sophisticated malware. They targeted tech giants like Nvidia, Microsoft, and Okta with surprising ease.

    Kurtaj was arrested, but the case took a tragic turn. He was deemed unfit for trial due to severe autism, yet a jury still convicted him based on evidence. In December 2023, he was sentenced to a hospital order—indefinite detention under mental health provisions. A second teenager was acquitted. The case raised uncomfortable questions: Should a minor with a disability be punished for a crime that caused tens of millions in damages? Or should he be treated as a victim of a system that failed him?

    The Fallout for Rockstar

    For developers, the leak was a personal violation. Work-in-progress footage—with debug menus, placeholder graphics, and glitches—was never meant for public eyes. Rockstar’s statement described the team’s distress: “We are extremely disappointed to have the details of our next game shared with everyone this way.”

    Beyond morale, the leak exposed security flaws. Rockstar had been using Slack channels without adequate multi-factor authentication, and the source code for GTA V and RDR2 was now in the wild. This code could be used to create cheats, exploit online services, or even build unauthorized mods. For a company that generates billions from GTA Online, that’s a serious threat.

    The creative impact was also a concern. Developers worried that showing unfinished work would lead to unfair comparisons with the final product, or force design changes to counter “leak fatigue.” Some fans, however, argued that the leak was harmless—a natural consequence of a decade of silence.

    The Fan Reaction: Excitement, Guilt, and Debate

    Among fans, the reaction was mixed. Many were thrilled to finally see something of GTA 6. The female protagonist—a first for the mainline series—was widely celebrated. Vice City’s return, set in a modern-day Miami, sparked nostalgia for the 2002 classic. The leak confirmed rumors that had circulated for years.

    But there was also guilt. A segment of the community refused to watch the footage, out of respect for the developers. Others argued that leaks are inevitable, and that Rockstar’s secrecy was itself the problem. The ethical debate divided the fanbase: Is it okay to consume leaked content if it harms the creators? The question has no easy answer.

    The Media’s Dilemma

    Major outlets like IGN and Kotaku covered the leak but avoided showing the raw footage. They linked to the leaked content sparingly, citing the ethical responsibility to not amplify a crime. Some journalists argued that reporting on the leak was newsworthy, but that hosting the footage crossed a line. Others said the public had a right to see what was happening.

    This tension continues today. Every time a game leaks, outlets must decide: report the facts, or risk becoming a distribution channel for stolen material? The GTA 6 leak set a precedent—one that many outlets still follow.

    What It Means for the Industry

    The GTA 6 leak wasn’t an anomaly. In 2023, Insomniac Games suffered a similar breach, with over 1.3 million files leaked, including details on upcoming games and employee data. The pattern is clear: game studios are prime targets for hackers, and the consequences are severe.

    For Rockstar, the leak didn’t delay the game—GTA 6 is still slated for 2025—but it forced a reevaluation of security. The company has since tightened its protocols, but the damage is done. The source code is out there, and the internet never forgets.

    As for Kurtaj, his case became a cautionary tale. He was a young man with a disability who fell into a world of cybercrime. His indefinite hospital order sparked debate about whether the justice system should treat minors as criminals or patients. In the end, the GTA 6 leak was a crime with real victims—the developers whose work was exposed, and a teenager who lost his freedom.

    The GTA 6 leak was a watershed moment for the gaming industry. It showed how vulnerable even the most secretive companies are, and how a single teenager could disrupt a billion-dollar franchise. For fans, it was a bittersweet gift: a glimpse of the future, tainted by the knowledge that it came at a cost. As GTA 6’s release approaches, the leaked footage will remain a reminder of what happens when the curtain is pulled back too early. The industry can only hope the next big leak doesn’t happen again.

    Summary

    • In September 2022, a hacker leaked over 90 videos and source code for GTA 6, causing widespread disruption.
    • The leak featured a female protagonist and a modern-day Vice City, confirming long-standing rumors.
    • The hacker was a 17-year-old from the Lapsus$ group, Arion Kurtaj, who was later sentenced to a hospital order.
    • Rockstar confirmed the leak was real and called it “extremely distressing,” while Take-Two’s stock dropped 6%.
    • The incident led to increased industry focus on security and raised ethical questions about leaked content.

    FAQ

    Q: Did the GTA 6 leak delay the game?
    A: No. Rockstar never confirmed a delay directly caused by the leak, and GTA 6 is still planned for 2025.

    Q: Who was the hacker behind the GTA 6 leak?
    A: A 17-year-old from Oxford, England, named Arion Kurtaj, who was part of the Lapsus$ hacking group. He was convicted and sentenced to a hospital order.

    Q: What was in the leaked GTA 6 footage?
    A: The footage showed early gameplay of a female protagonist named Lucia, set in a modern-day Vice City, with unfinished animations and placeholder graphics.

    Q: Was the leaked GTA 6 footage real?
    A: Yes, Rockstar Games confirmed the leak was authentic, though the footage was from an early development build.

    Q: How did the gaming media handle the GTA 6 leak?
    A: Most major outlets covered the news but avoided showing the raw footage, citing ethical concerns about amplifying stolen content.

  • Lattice-Based Cryptography: The Math That Will Survive Quantum Computers

    Lattice-Based Cryptography: The Math That Will Survive Quantum Computers

    Imagine trying to find the shortest path in a maze where the walls keep shifting. That’s the core challenge behind lattice-based cryptography, a family of algorithms designed to be secure even against quantum computers. As quantum technology advances, the encryption that protects your emails, bank transactions, and private messages is at risk. Lattice-based cryptography offers a mathematical solution that could keep your data safe in the quantum age.

    This article explains how lattice-based cryptography works, why it’s considered quantum-resistant, and how it’s already being deployed to protect the internet’s future. We’ll break down the complex math into simple analogies, look at the real-world standards being adopted, and address common questions about this critical technology.

    The Quantum Threat to Modern Encryption

    Most of the internet’s security relies on math problems that are easy to do but hard to undo. For example, it’s easy to multiply two large prime numbers, but given their product, finding those primes is incredibly time-consuming. This is the basis of RSA encryption.

    Quantum computers, however, change the game. In 1994, mathematician Peter Shor developed an algorithm that could factor large numbers efficiently on a quantum computer. This means RSA, along with other popular methods like Elliptic Curve Cryptography (ECC), would be broken. An attacker with a sufficiently powerful quantum computer could decrypt intercepted messages, forge signatures, and impersonate websites.

    This isn’t just a theoretical concern. Security agencies warn about “harvest now, decrypt later” attacks, where adversaries collect encrypted data today, anticipating that they’ll be able to decrypt it in the future. The clock is ticking for a solution.

    What Are Lattices? A Simple Analogy

    A lattice is a mathematical structure that looks like an infinite grid of points in space. Think of a 2D lattice as a sheet of graph paper extending infinitely in all directions, with points at every intersection. In higher dimensions, lattices become abstract but follow the same principle: a repeating, regular arrangement of points.

    The security of lattice-based cryptography relies on two hard problems:

    • Shortest Vector Problem (SVP): Given a lattice, find the shortest non-zero vector (the shortest distance from one point to another).
    • Closest Vector Problem (CVP): Given a lattice and a target point, find the lattice point closest to that target.

    These problems sound simple, but they become incredibly hard in high dimensions. There is no known efficient algorithm, even for quantum computers, to solve them. This is the foundation of lattice-based security.

    The Magic of Noise: Learning With Errors

    Modern lattice-based schemes build on a problem called Learning With Errors (LWE), introduced by Oded Regev in 2005. Here’s the idea:

    Imagine you have a secret vector (a list of numbers) that you want to keep private. You create equations that relate this secret to other numbers, but you intentionally add small, random errors to the equations. Solving the system without knowing the exact errors is nearly impossible. The errors act like a fog that hides the secret.

    This “noise” is controlled — it’s small enough that someone with the correct key can filter it out, but large enough that an attacker cannot. This clever trick makes LWE-based encryption both secure and practical.

    NIST’s Selection: The New Standards

    In 2016, the U.S. National Institute of Standards and Technology (NIST) launched a global competition to find post-quantum cryptographic algorithms. After years of evaluation, in August 2024, NIST published final standards for four algorithms:

    • ML-KEM (based on CRYSTALS-Kyber) for key encapsulation, which is used to establish shared secrets securely.
    • ML-DSA (based on CRYSTALS-Dilithium) and FN-DSA (based on Falcon) for digital signatures.
    • SLH-DSA (based on SPHINCS+) is a hash-based backup, not lattice-based, but included for diversity.

    These standards are now the go-to recommendations for organizations looking to secure their systems against quantum threats.

    Real-World Adoption: Already Happening

    Lattice-based cryptography isn’t just theory — it’s being deployed. Companies like Google, Cloudflare, and Amazon have been testing hybrid schemes that combine classical and post-quantum algorithms to ensure compatibility and security during the transition.

    One notable example is Signal, the messaging app, which uses a protocol called PQXDH that incorporates Kyber. This means your private messages are already protected against future quantum attacks. Similarly, Linux distributions and web browsers are beginning to support these new algorithms.

    The transition is gradual because it requires updating infrastructure worldwide. But the momentum is real, and lattice-based cryptography is leading the charge.

    Performance and Trade-offs

    One reason lattice-based schemes are favored is their efficiency. They have relatively small key sizes and fast operations compared to other post-quantum families like code-based or hash-based cryptography. However, they are still larger and slower than RSA or ECC, which could be a concern for devices with limited resources, like IoT sensors.

    Researchers are actively working on optimizing implementations and reducing overhead. There’s also ongoing debate about parameter choices and side-channel resistance, but so far, lattice-based schemes are considered robust.

    The Future: Beyond Encryption

    Lattice-based cryptography also enables advanced features that classical methods cannot easily provide, such as fully homomorphic encryption (FHE). FHE allows computations on encrypted data without decrypting it, which could revolutionize cloud computing and data privacy.

    As quantum computing research progresses, the need for quantum-safe cryptography will only grow. Lattice-based methods offer a versatile and secure foundation for the post-quantum world.

    Lattice-based cryptography is not just a stopgap but a long-term solution for securing our digital future. With NIST’s standards in place and companies already integrating these algorithms, the shift to quantum-safe encryption is underway. By understanding the basic principles behind lattices and LWE, you can appreciate the elegance of this solution and why it gives us confidence in the face of quantum threats.

    Summary

    • Lattice-based cryptography relies on hard math problems (SVP, CVP) that even quantum computers can’t solve efficiently.
    • The Learning With Errors (LWE) problem introduces controlled noise, making encryption secure and practical.
    • NIST selected ML-KEM, ML-DSA, and FN-DSA as lattice-based standards in August 2024.
    • Real-world deployment is already happening, with Signal, Google, and Cloudflare testing or using lattice-based algorithms.
    • These schemes offer a good balance of security, performance, and versatility, including advanced features like fully homomorphic encryption.

    FAQ

    Q: What is a lattice in simple terms?
    A: A lattice is like an infinite grid of points in space. Think of graph paper extending forever, but in higher dimensions. The security relies on how hard it is to find the shortest distance between points or the closest point to a target.

    Q: Why are current encryption methods vulnerable to quantum computers?
    A: Shor’s algorithm can efficiently factor large numbers and solve discrete logarithms, which breaks RSA and ECC. Lattice problems don’t have such efficient quantum solutions.

    Q: Is lattice-based cryptography already in use?
    A: Yes, it’s being rolled out. For example, Signal messaging uses Kyber, and NIST published final standards in 2024 that companies are adopting.

    Q: Are lattice-based algorithms slower than traditional ones?
    A: They’re a bit larger and slower than RSA/ECC, but still efficient enough for most applications. Researchers are working on optimizations for constrained devices.

    Q: Can lattice-based encryption be broken by future quantum computers?
    A: No known algorithm exists, but cryptographers continuously analyze the schemes. That’s why NIST chose multiple algorithms and encourages crypto agility — to be able to switch if one is ever broken.

  • Norway’s Digital Frontline: Understanding the Ongoing DDoS Attack on Government Services

    Norway’s Digital Frontline: Understanding the Ongoing DDoS Attack on Government Services

    Imagine trying to file your taxes, check your health records, or sign a business document online, only to find that the website won’t load. For many Norwegians, this is not a hypothetical scenario—it’s happening right now. The Norwegian Digitalisation Agency (Digdir) is currently battling a Distributed Denial of Service (DDoS) attack against the country’s central government IT infrastructure, causing disruptions to essential digital services.

    This attack is not just a technical inconvenience; it’s a stark reminder of how dependent modern societies have become on a handful of digital gateways. In Norway, those gateways are operated by Digdir, a single agency that provides shared services like ID-porten (the login system for public services) and Altinn (the portal for business reporting). When these systems go down, the ripple effects are felt across the entire country—from citizens trying to access healthcare to businesses meeting tax deadlines.

    In this article, we’ll break down what a DDoS attack is, why Norway’s centralized e-government model makes it a prime target, and what the ongoing incident means for citizens, businesses, and national security. We’ll also look at the broader context of cyber threats facing Norway and how the government is responding.

    What Is a DDoS Attack, Anyway?

    A Distributed Denial of Service (DDoS) attack is like a traffic jam caused by thousands of cars flooding a single highway. In the digital world, the “cars” are data requests, and the “highway” is a server or network. The attacker sends an overwhelming amount of traffic to a target, clogging its bandwidth or exhausting its resources, so that legitimate users can’t get through.

    Think of it this way: if a popular coffee shop only has one barista, and a prankster sends 100 friends to order drinks at the same time, the barista becomes overwhelmed, and real customers have to wait or leave. In a DDoS attack, the prankster uses a botnet—a network of hijacked computers or devices—to send millions of requests, effectively shutting down the service.

    There are different types of DDoS attacks: volumetric (flooding bandwidth), protocol-based (exhausting server resources), and application-layer (targeting specific functions like login forms). The exact method used against Norway hasn’t been publicly detailed, but the effect is clear: services are degraded or completely unavailable.

    Why Norway’s E-Government Is a High-Value Target

    Norway has one of the most centralized digital government systems in the world. Instead of each agency running its own IT, most public services rely on shared components operated by Digdir. This includes:

    • ID-porten: The single sign-on system for all public services. If you’re a Norwegian citizen, you use this to log in to everything from tax forms to healthcare portals.
    • Altinn: The main portal for businesses to report data to authorities, such as tax returns, VAT, and annual accounts.
    • Digital mailbox: Services like Digipost and e-Boks, where citizens receive official letters from the government.

    This centralization is efficient and cost-effective, but it also creates a single point of failure. If an attacker can take down Digdir’s infrastructure, they can disrupt a huge portion of the public sector at once. It’s like knocking out the power grid for a whole city instead of just one neighborhood.

    The Current Attack: What We Know

    The attack is ongoing, and the authoritative source for updates is Digdir’s status page (status.digdir.no). As of the latest reports, the status page shows “Degraded performance” or “Major outage” for various services, meaning some users may be unable to log in or access certain functions.

    The incident has also caught the attention of the tech community, with discussions on Hacker News highlighting the significance of the attack. While no official attribution has been made, Norway has been a target of pro-Russian hacktivist groups in the past, especially in response to its support for Ukraine. However, attribution is often murky, and attacks can be carried out by various actors using rented DDoS-for-hire services.

    How Is Norway Responding?

    When a DDoS attack hits, the immediate goal is to mitigate the impact and restore services. Digdir works with internet service providers and security agencies like the National Security Authority (NSM) to filter out malicious traffic. Common techniques include:

    • Traffic scrubbing: Redirecting incoming traffic through a cleaning center that filters out malicious requests before they reach the server.
    • Rate limiting: Slowing down or blocking requests from suspicious sources.
    • Load balancing: Distributing traffic across multiple servers to prevent any single one from being overwhelmed.

    These measures can help, but they’re not always perfect. The attack is ongoing, which suggests that the perpetrators are persistent or adapting their methods.

    The Human Impact: What It Means for Citizens and Businesses

    For ordinary Norwegians, the attack can be more than an inconvenience. Imagine needing to access your medical records or submit a tax form by a deadline, only to find the system down. For businesses, Altinn is critical for regulatory compliance—missing a filing deadline can result in fines or legal issues.

    The attack also raises questions about the resilience of Norway’s digital society. If a single DDoS can disrupt so many services, what happens in a more severe cyber incident? This incident serves as a wake-up call, highlighting the need for robust cybersecurity measures and perhaps even a more decentralized approach to critical infrastructure.

    A History of Cyber Threats in Norway

    This is not the first time Norway has faced such attacks. In 2023, the Norwegian Parliament and several ministries were hit by DDoS attacks, attributed to pro-Russian groups like Killnet and Anonymous Sudan. In 2024, the Labour and Welfare Administration (NAV) and the Directorate of Health experienced outages. The current attack appears to be a continuation of this pattern, suggesting that Norway is a persistent target in the geopolitical cyber landscape.

    These attacks are often seen as hybrid threats—actions that fall below the threshold of open warfare but are designed to test a nation’s resilience and sow chaos. Norway’s response, including cooperation with NATO’s Cyber Defence Centre, is part of a broader strategy to defend against such threats.

    Looking Ahead: Lessons for Other Nations

    The Norwegian experience offers valuable lessons for other countries with centralized digital infrastructure. While centralization brings efficiency, it also concentrates risk. Diversifying critical systems, investing in robust DDoS protection, and having clear incident response plans are essential.

    For citizens, the incident is a reminder of the importance of cybersecurity awareness. While individuals can’t prevent DDoS attacks, they can advocate for stronger protections and be prepared for potential disruptions.

    As the attack continues, the world is watching how Norway handles this digital siege. The outcome will not only affect Norwegian citizens but also shape how other nations approach the security of their own e-government systems.

    The ongoing DDoS attack on Norway’s government IT infrastructure is a stark reminder of the fragility of our digital world. It shows how a single attack can disrupt essential services and highlights the need for robust cybersecurity measures. While Digdir works to restore services, the incident underscores the importance of resilience, both in technology and in public awareness. As Norway navigates this crisis, the rest of the world can learn from its experience—and hope that such attacks become less frequent, not more.

    Summary

    • A DDoS attack is currently targeting Norway’s central government IT infrastructure, operated by Digdir, causing disruptions to services like ID-porten and Altinn.
    • Norway’s centralized e-government model makes it a high-value target, as a single attack can affect many public services at once.
    • The attack is ongoing, with no official attribution, but it follows a pattern of similar incidents in recent years, often linked to pro-Russian hacktivist groups.
    • Mitigation efforts include traffic filtering, rate limiting, and load balancing, coordinated by Digdir with security agencies.
    • The incident highlights the importance of cybersecurity resilience and the potential risks of over-centralization in digital infrastructure.

    FAQ

    Q: What is a DDoS attack?
    A: A Distributed Denial of Service (DDoS) attack is an attempt to overwhelm a server or network with a flood of internet traffic, making it unavailable to legitimate users. It’s like a traffic jam caused by too many cars on a road.

    Q: Which Norwegian services are affected?
    A: The attack targets shared government platforms operated by Digdir, including ID-porten (login for public services), Altinn (business reporting), and digital mailbox services. The status page at status.digdir.no provides real-time updates.

    Q: Who is behind the attack?
    A: No official attribution has been made. Historically, pro-Russian hacktivist groups have claimed responsibility for similar attacks on Norway, but attribution is often uncertain and could be politically motivated.

    Q: How is Norway responding?
    A: Digdir is working with internet service providers and security agencies like the National Security Authority (NSM) to filter malicious traffic, rate-limit requests, and balance loads across servers. The goal is to restore services as quickly as possible.

    Q: What can citizens do during the outage?
    A: Citizens should monitor the status page for updates and try again later. For critical deadlines, it’s advisable to contact the relevant agency directly. In general, patience and awareness are key during such incidents.